Slides / 13 of 19
Talk slides
The value of security tools: what we wouldn't have if we had everything
Nikita Vyugin · MKO Systems
Day 2 — Friday, 12 September 2025: information security day · Scheduled 13:10–13:40 · In the recording 05:48:22–06:35:13
These slides are an English version of the Russian deck shown in the recording: the text the authors set in the presentation has been translated and redrawn in place, while everything captured from a screen — program windows, logs, evidence — is left exactly as it was, in Russian. The fonts are the closest available ones, not the originals. The Russian deck is on the RU version of this page. Under each slide its text is set out for word search and machine reading.
Page 105:49:38 Slide text
THE VALUE OF SECURITY TOOLS: WHAT WE WOULDN'T HAVE IF WE HAD EVERYTHING
Page 205:50:11 Slide text
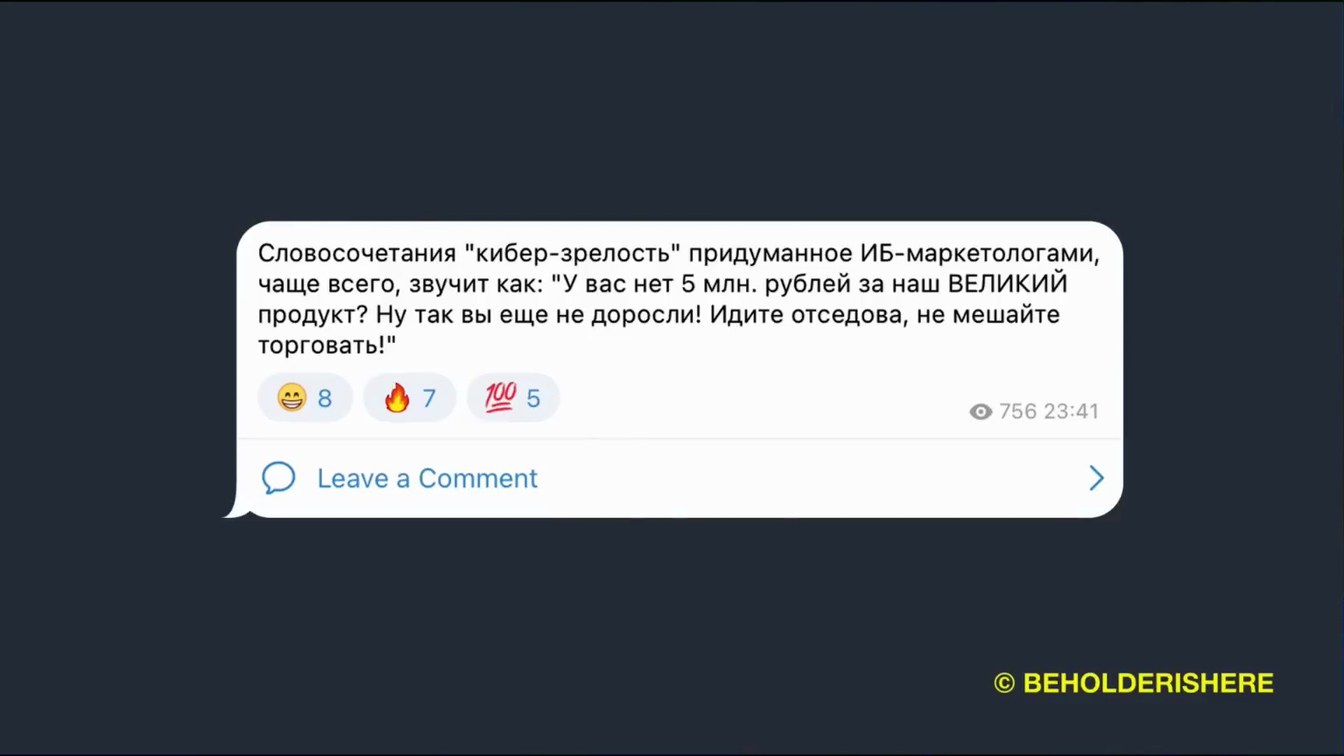
Словосочетания "кибер-зрелость" придуманное ИБ-маркетологами, чаще всего, звучит как: "У вас нет 5 млн. рублей за наш ВЕЛИКИЙ продукт? Ну так вы еще не доросли! Идите отседова, не мешайте торговать!"
7
100 5
• 756 23:41
Leave a Comment
© BEHOLDERISHERE
Page 305:50:44 Slide text
DASARCASM
Page 405:51:54 Slide text
MYTHS OF REASONABLENESS AND MATURITY
Page 505:53:19 Slide text
ANTIVIRUS
DLP
Antivirus finds, blocks and removes malware.
Antivirus is the basic level of endpoint protection: users, office machines, servers. The very first step in a cybersecurity strategy.
EDR/XDR
SIEM
SOAR
SOC
DFIR
Page 605:54:43 Slide text
ANTIVIRUS
NUANCES:
False positives
DLP
False sense of security
EDR/XDR
Limited detection
SIEM
Poor integration with other security tools
• BYOD
SOAR
Difficulties in investigating incidents
SOC
DFIR
Page 705:56:00 Slide text
ANTIVIRUS
DLP
WHAT AWAITS US WITHOUT ANTIVIRUS:
Simple threats won't be blocked right away
Higher load on other security systems
EDR/XDR
Increased risk of infection “from below”
SIEM
Loss of the basic level of compliance
Financial and reputational consequences
SOAR
SOC
DFIR
Page 805:56:31 Slide text
This is the foundation, the basics. If your company uses even one digital device — you need an antivirus.
Page 905:58:01 Slide text
ANTIVIRUS
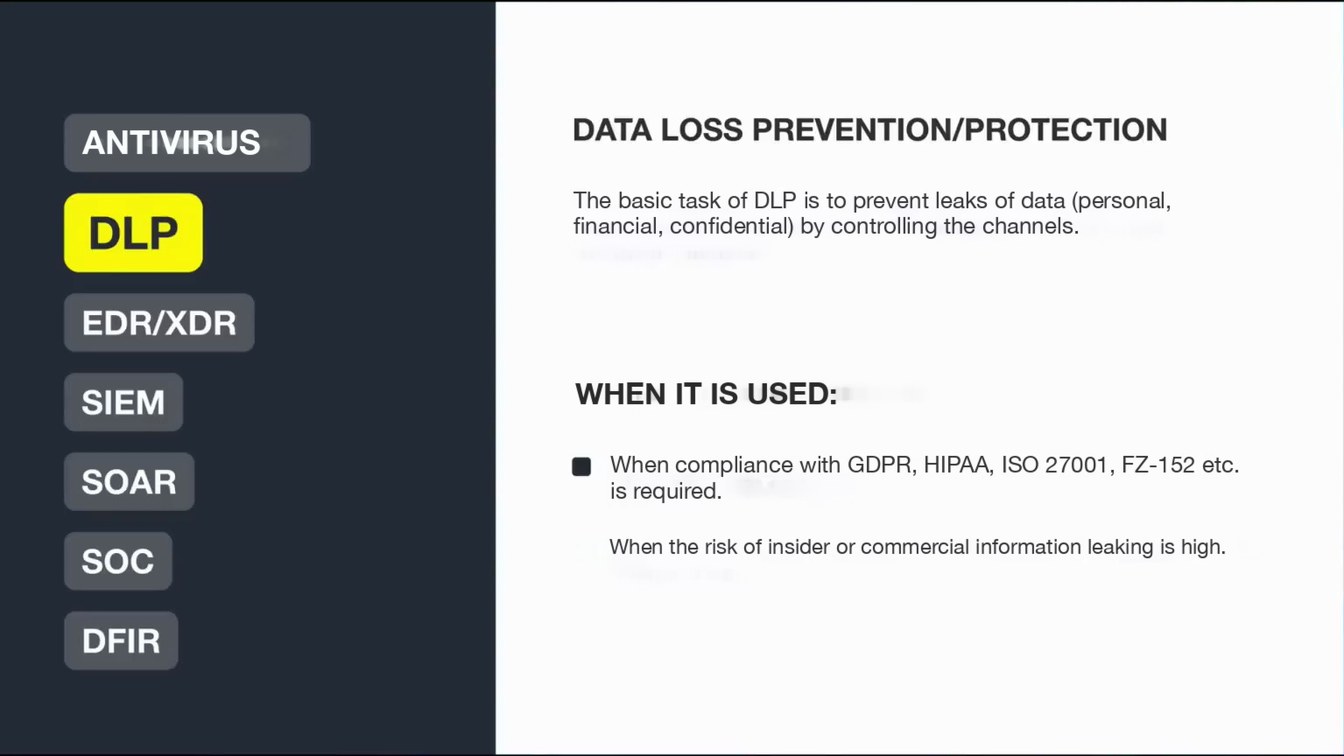
DATA LOSS PREVENTION/PROTECTION
DLP
The basic task of DLP is to prevent leaks of data (personal, financial, confidential) by controlling the channels.
EDR/XDR
SIEM
WHEN IT IS USED:
SOAR
When compliance with GDPR, HIPAA, ISO 27001, FZ-152 etc. is required.
SOC
When the risk of insider or commercial information leaking is high.
DFIR
Page 1005:59:04 Slide text
ANTIVIRUS
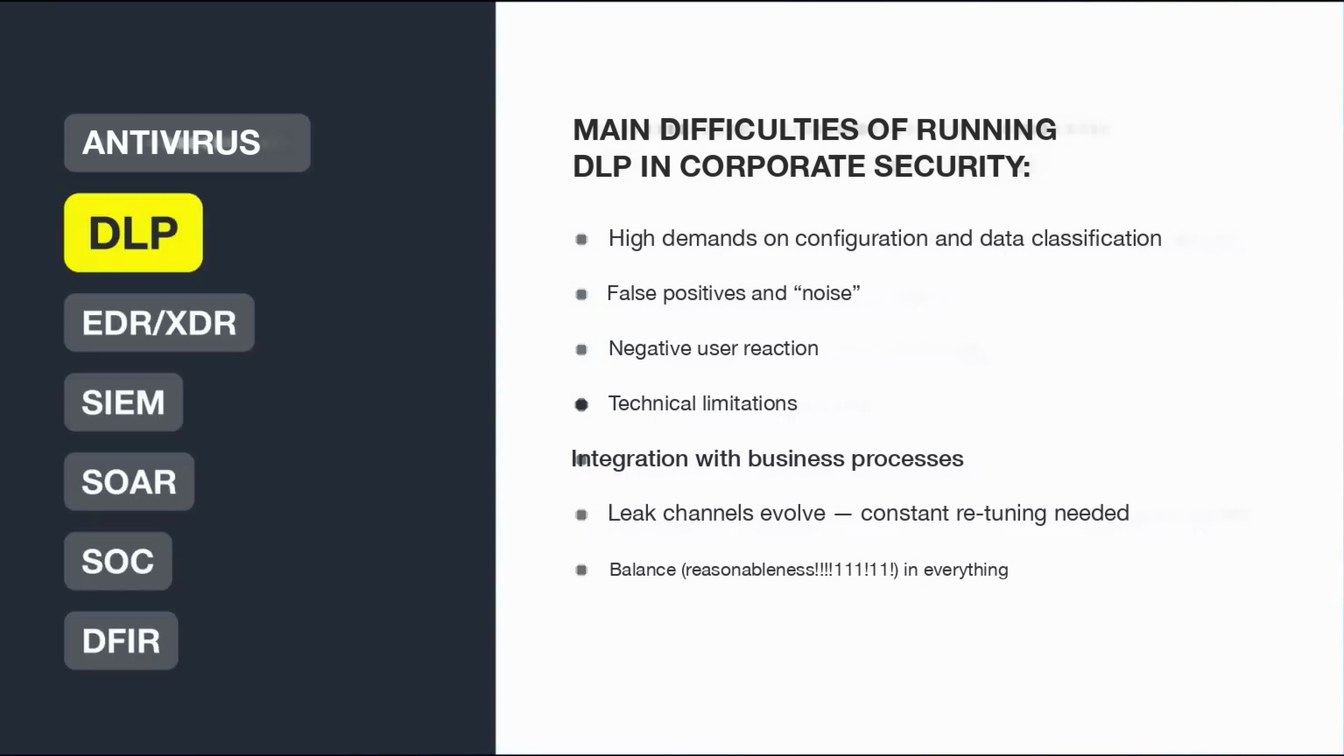
MAIN DIFFICULTIES OF RUNNING DLP IN CORPORATE SECURITY:
DLP
High demands on configuration and data classification
EDR/XDR
False positives and “noise”
Negative user reaction
SIEM
Technical limitations
SOAR
Integration with business processes
Leak channels evolve — constant re-tuning needed
SOC
Balance (reasonableness!!!!111!11!) in everything
DFIR
Page 1106:00:07 Slide text
ANTIVIRUS
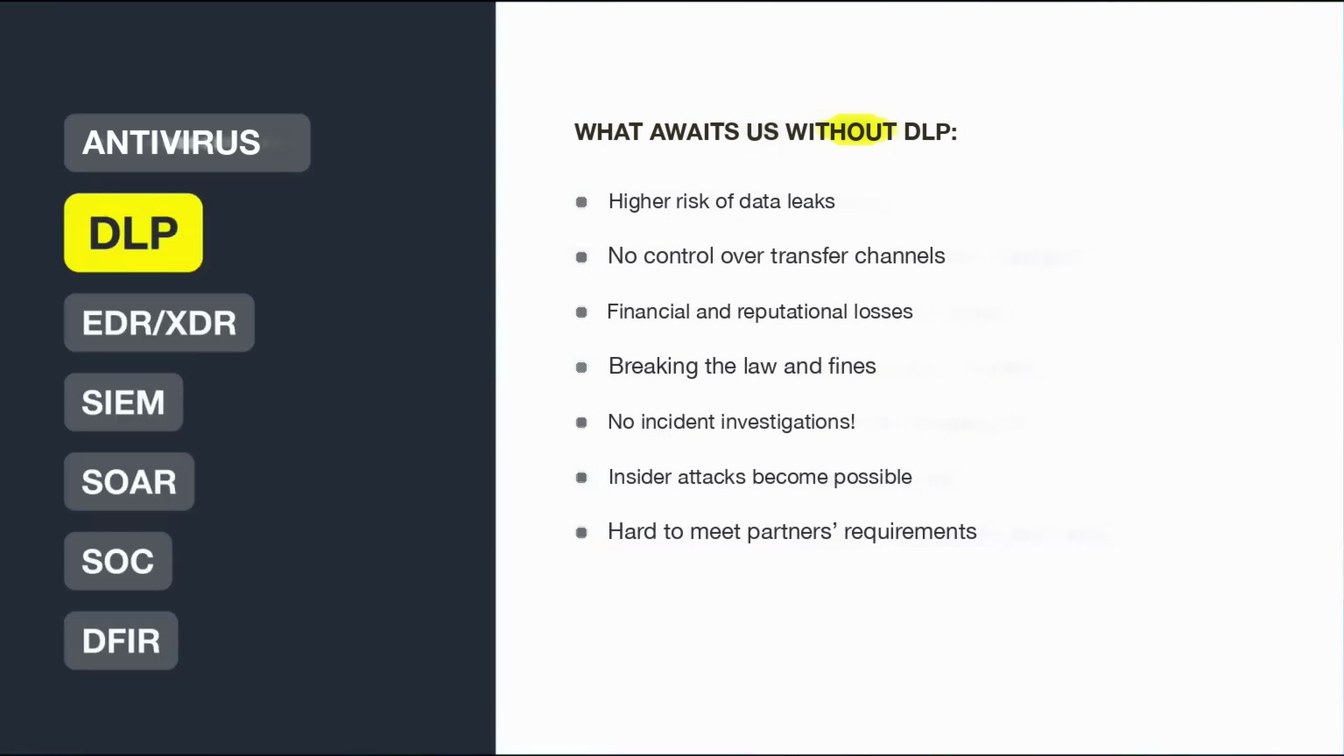
WHAT AWAITS US WITHOUT DLP:
DLP
Higher risk of data leaks
No control over transfer channels
EDR/XDR
Financial and reputational losses
SIEM
Breaking the law and fines
No incident investigations!
SOAR
Insider attacks become possible
SOC
Hard to meet partners’ requirements
DFIR
Page 1206:00:33 Slide text
DLP is good and important!
DLP put in “with the spare change” is bad — eats money, creates problems.
Page 1306:01:29 Slide text
ANTIVIRUS
DLP
Endpoint Detection and Response (EDR) — monitors PCs and servers, but does it a bit more interestingly than antivirus: it records process behaviour, network connections, script launches and so on.
EDR/XDR
SIEM
Extended Detection and Response (XDR) — a larger-scale EDR. It uses the network, email, clouds etc. as data sources, correlates events across systems and provides a single console for management and investigation.
SOAR
SOC
DFIR
Page 1406:03:00 Slide text
ANTIVIRUS
EDR/XDR NUANCES IN CORPORATE SECURITY:
DLP
Noise and alert overload
Complex to deploy and configure
EDR/XDR
High demands on staff competence
SIEM
Integration with other systems
Balance between security and user convenience
SOAR
Expensive to scale (and you will have to!!!)
SOC
DFIR
Page 1506:04:10 Slide text
ANTIVIRUS
WHAT AWAITS US WITHOUT EDR/XDR:
DLP
Poor visibility of endpoints
Late detection of incidents
EDR/XDR
Investigation difficulties (DFIR)
SIEM
Ineffective SOC
Growing damage from attacks
SOAR
Failure to meet modern security standards
SOC
DFIR
Page 1606:04:48 Slide text
EDR and XDR are powerful tools for protecting corporate infrastructure that provide a high level of security. But before deploying them it is important to weigh carefully all the pros and cons, and the company’s readiness for such changes.
Page 1706:06:02 Slide text
ANTIVIRUS
SECURITY INFORMATION & EVENT
MANAGEMENT
DLP
EDR/XDR
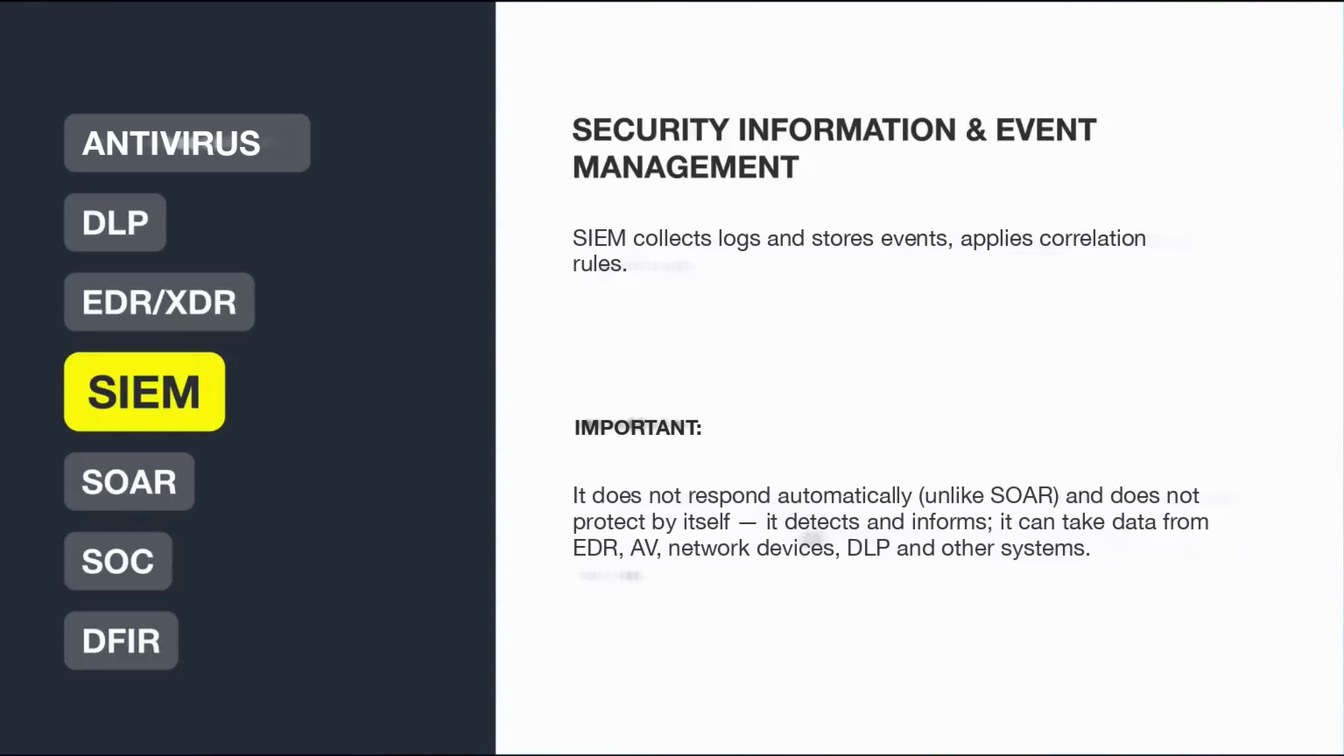
SIEM collects logs and stores events, applies correlation rules.
SIEM
IMPORTANT:
SOAR
SOC
It does not respond automatically (unlike SOAR) and does not protect by itself — it detects and informs; it can take data from EDR, AV, network devices, DLP and other systems.
DFIR
Page 1806:07:47 Slide text
ANTIVIRUS
THORNS ON THE WAY TO SIEM:
DLP
“Garbage” at the input
Detailed rules have to be written for your infrastructure
EDR/XDR
SIEM
You must be sure you have the resources for manual or automatic response to SIEM’s call, otherwise there is no point
SOAR
SOC
DFIR
Page 1906:08:57 Slide text
ANTIVIRUS
WHAT AWAITS US WITHOUT SIEM:
DLP
No single picture of security events
Poor real-time visibility of attacks
EDR/XDR
SOC goes “blind”
SIEM
Investigations become hard (DFIR)
Failure to meet requirements and standards
SOAR
SOC
DFIR
Page 2006:09:41 Slide text
At scale, without SIEM a company effectively loses the central brain of monitoring. All the other systems work, but each on its own, and the business has no full security picture.
Page 2106:12:40 Slide text
ANTIVIRUS
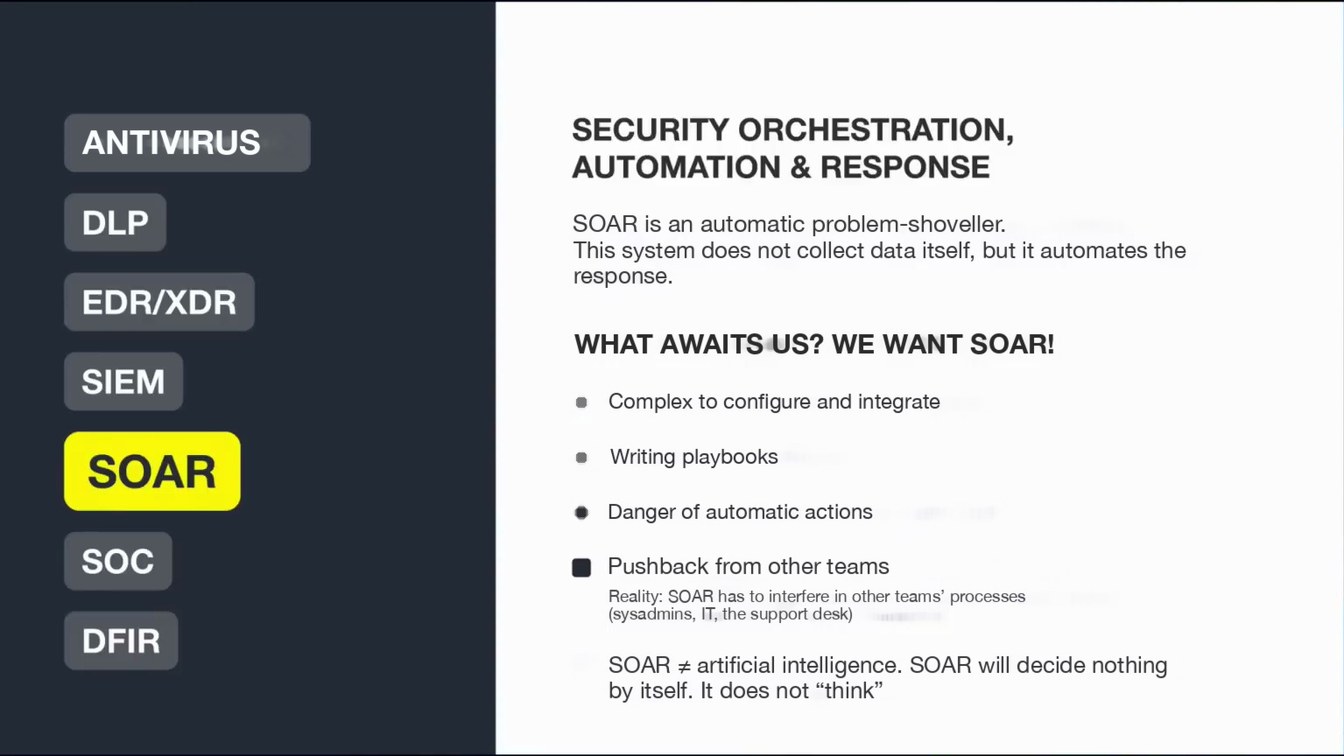
SECURITY ORCHESTRATION, AUTOMATION & RESPONSE
DLP
EDR/XDR
SIEM
SOAR is an automatic problem-shoveller.
This system does not collect data itself, but it automates the response.
WHAT AWAITS US? WE WANT SOAR!
Complex to configure and integrate
SOAR
Writing playbooks
Danger of automatic actions
SOC
DFIR
Pushback from other teams
Reality: SOAR has to interfere in other teams’ processes (sysadmins, IT, the support desk)
SOAR ≠ artificial intelligence. SOAR will decide nothing by itself. It does not “think”
Page 2206:14:04 Slide text
ANTIVIRUS
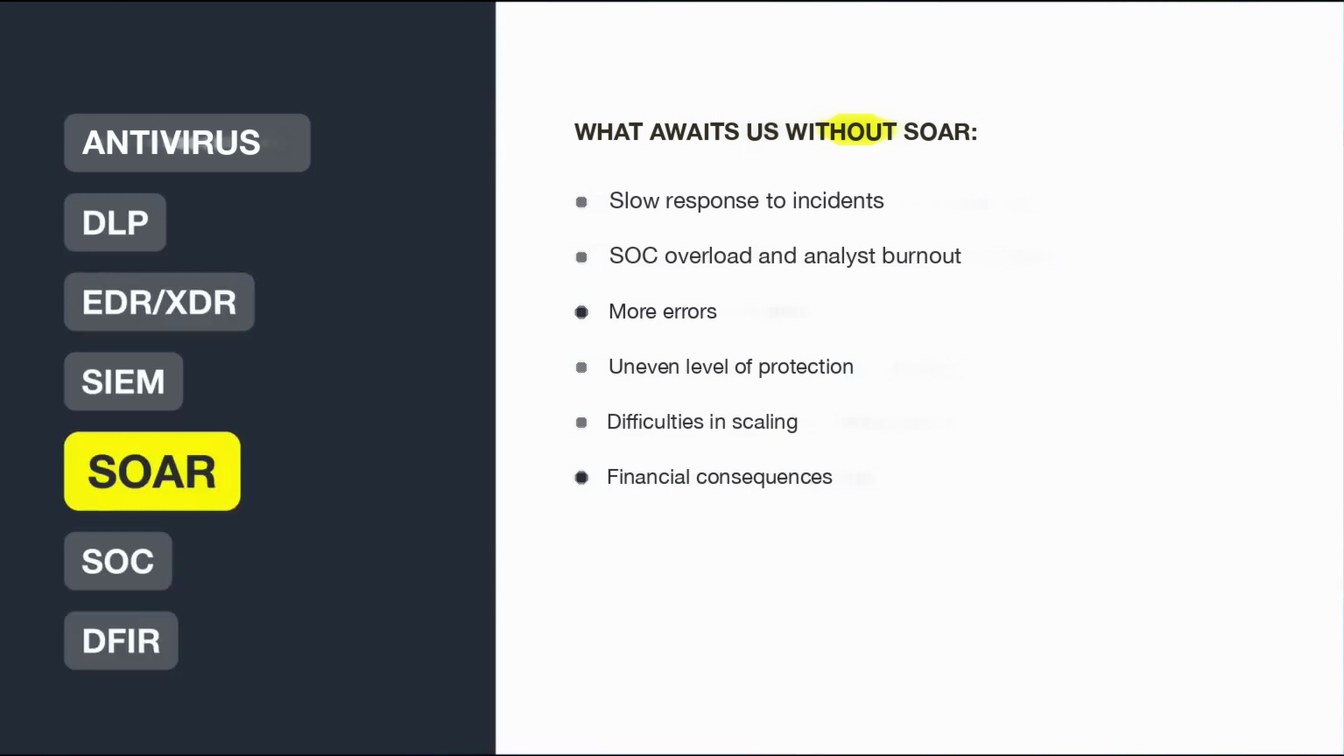
WHAT AWAITS US WITHOUT SOAR:
DLP
Slow response to incidents
SOC overload and analyst burnout
EDR/XDR
More errors
SIEM
Uneven level of protection
Difficulties in scaling
SOAR
Financial consequences
SOC
DFIR
Page 2306:15:05 Slide text
ANTIVIRUS
SECURITY OPERATION CENTER
DLP
EDR/XDR
SOC is an information security monitoring centre. An organizational unit that receives signals from everywhere, sorts through them and responds accordingly.
SIEM
SOAR
SOC
DFIR
GREAT AND TERRIBLE!!!
Page 2406:16:22 Slide text
ANTIVIRUS
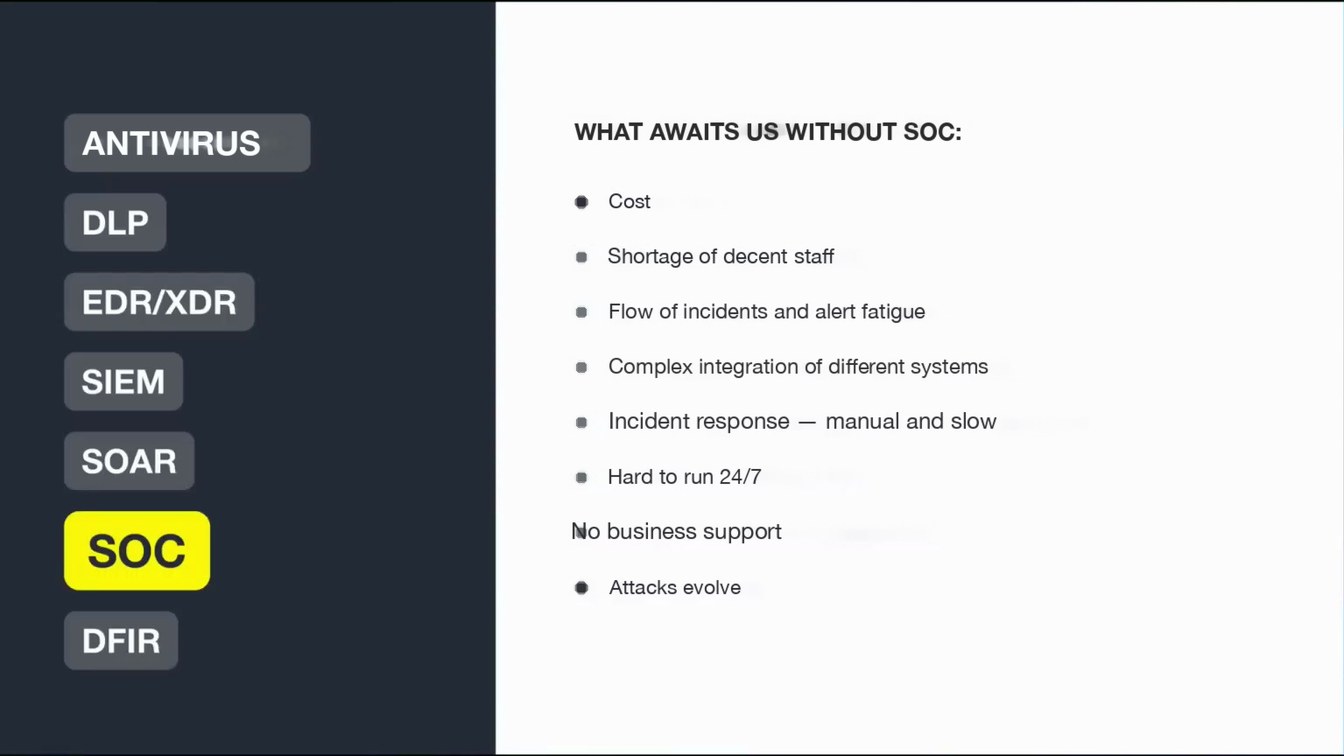
WHAT AWAITS US WITHOUT SOC:
DLP
Cost
Shortage of decent staff
EDR/XDR
Flow of incidents and alert fatigue
SIEM
SOAR
Complex integration of different systems
Incident response — manual and slow
Hard to run 24/7
SOC
No business support
Attacks evolve
DFIR
Page 2506:17:25 Slide text
ANTIVIRUS
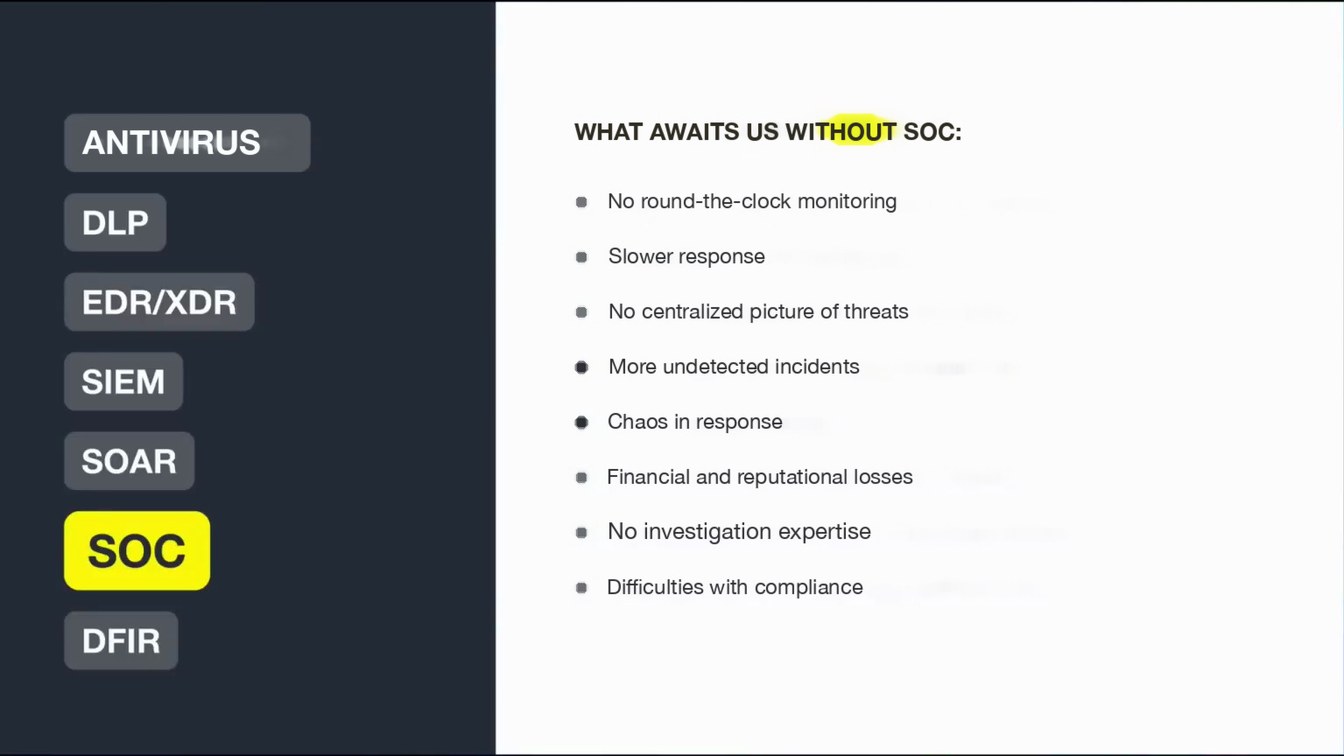
WHAT AWAITS US WITHOUT SOC:
DLP
No round-the-clock monitoring
Slower response
EDR/XDR
No centralized picture of threats
SIEM
More undetected incidents
SOAR
Chaos in response
Financial and reputational losses
SOC
No investigation expertise
Difficulties with compliance
DFIR
Page 2606:17:52 Slide text
SOC is not an “option” but a necessary element of mature cyber defence at a certain scale.
A successful SOC = a balance of technologies (SIEM, SOAR, EDR/XDR, DLP), processes and people.
Page 2706:18:47 Slide text
ANTIVIRUS
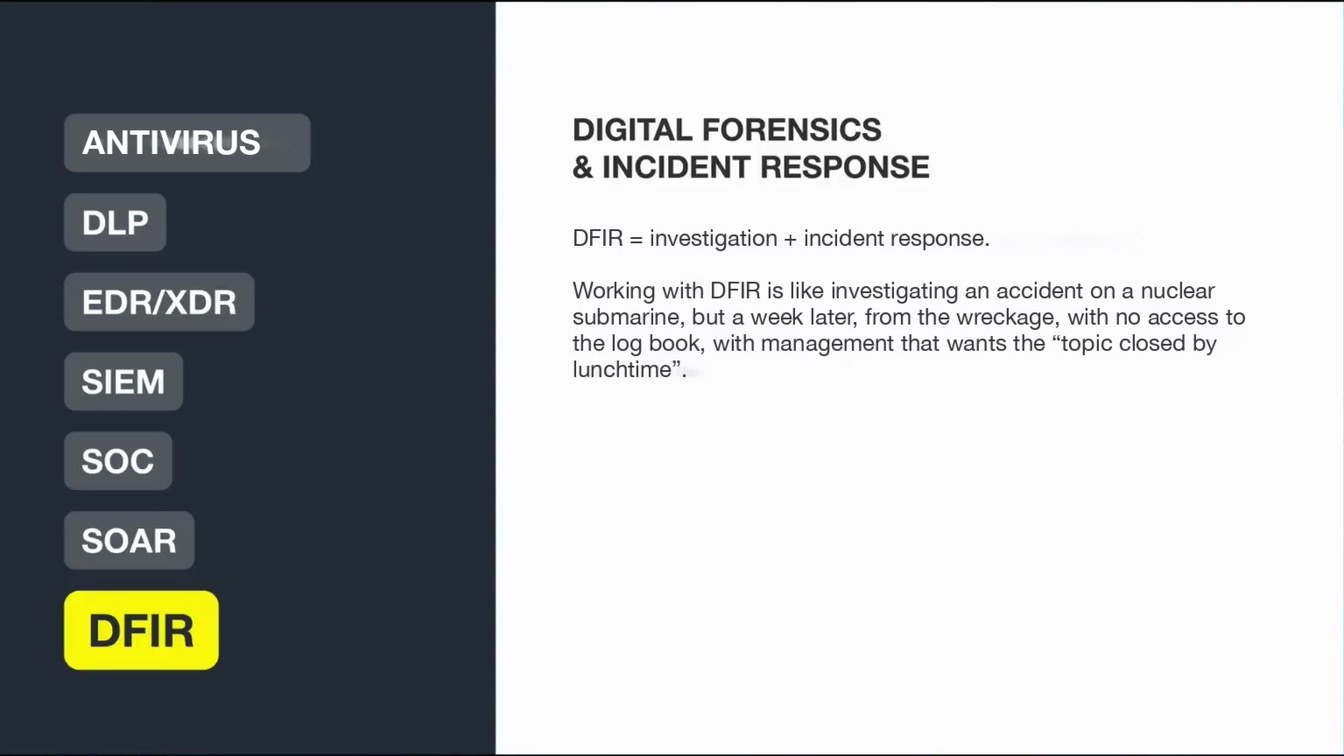
DIGITAL FORENSICS & INCIDENT RESPONSE
DLP
DFIR = investigation + incident response.
SIEM
Working with DFIR is like investigating an accident on a nuclear submarine, but a week later, from the wreckage, with no access to the log book, with management that wants the “topic closed by lunchtime”.
SOC
SOAR
DFIR
Page 2806:20:11 Slide text
ANTIVIRUS
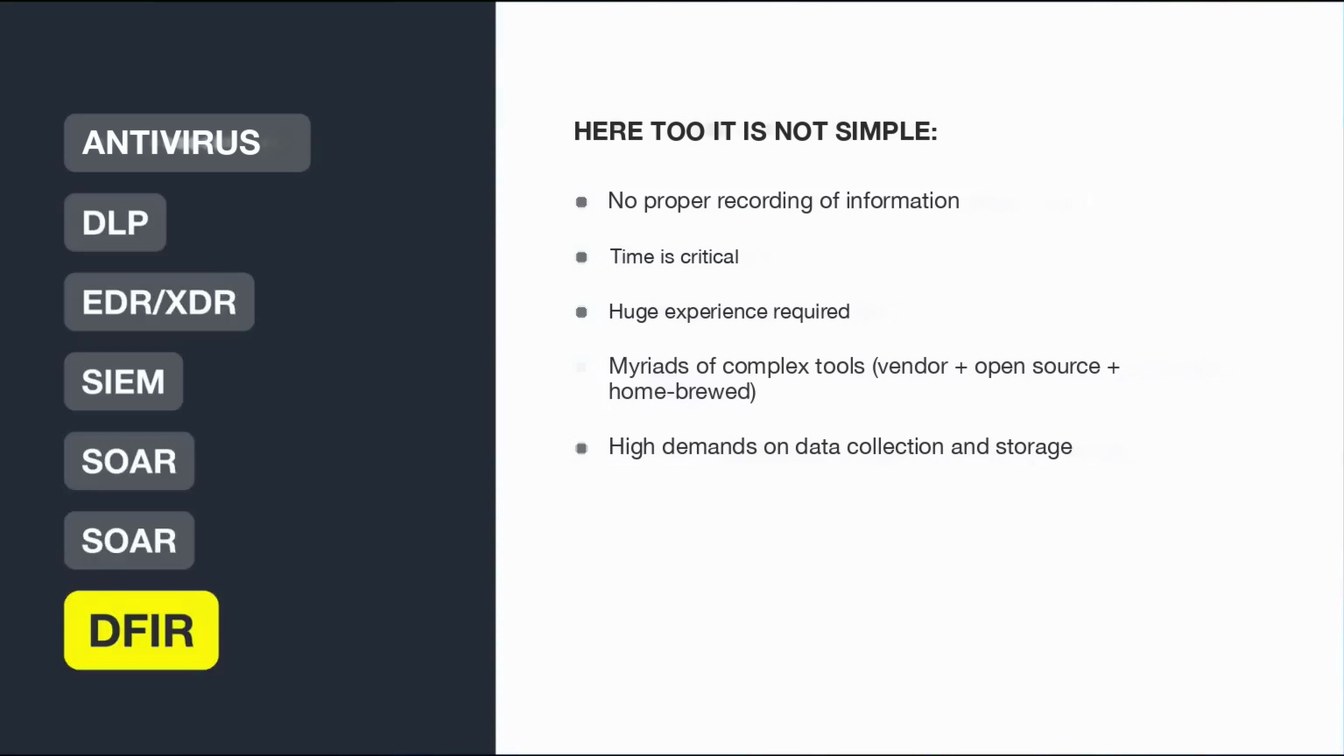
HERE TOO IT IS NOT SIMPLE:
DLP
No proper recording of information
Time is critical
EDR/XDR
Huge experience required
SIEM
Myriads of complex tools (vendor + open source + home-brewed)
SOAR
High demands on data collection and storage
SOAR
DFIR
Page 2906:22:17 Slide text
ANTIVIRUS
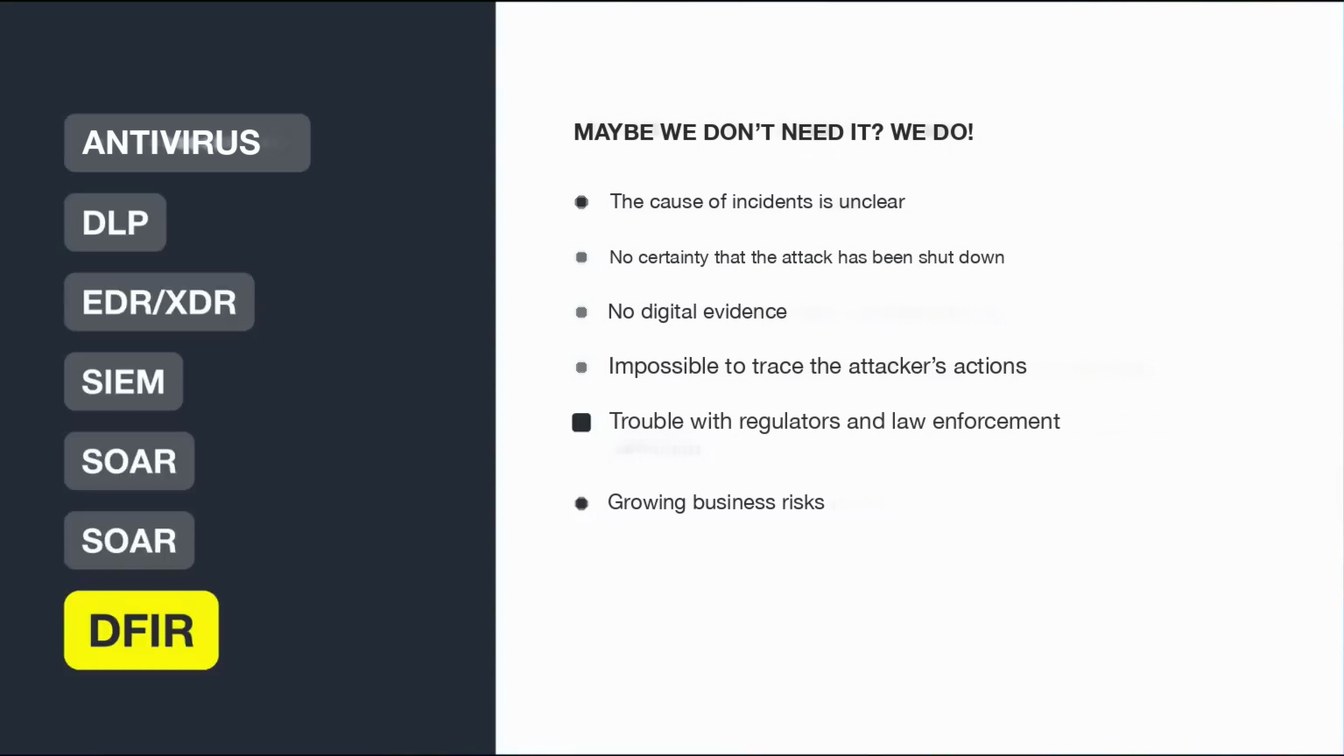
MAYBE WE DON’T NEED IT? WE DO!
DLP
EDR/XDR
The cause of incidents is unclear
No certainty that the attack has been shut down
No digital evidence
SIEM
SOAR
Impossible to trace the attacker’s actions
Trouble with regulators and law enforcement
SOAR
Growing business risks
DFIR
Page 3006:23:59 Slide text
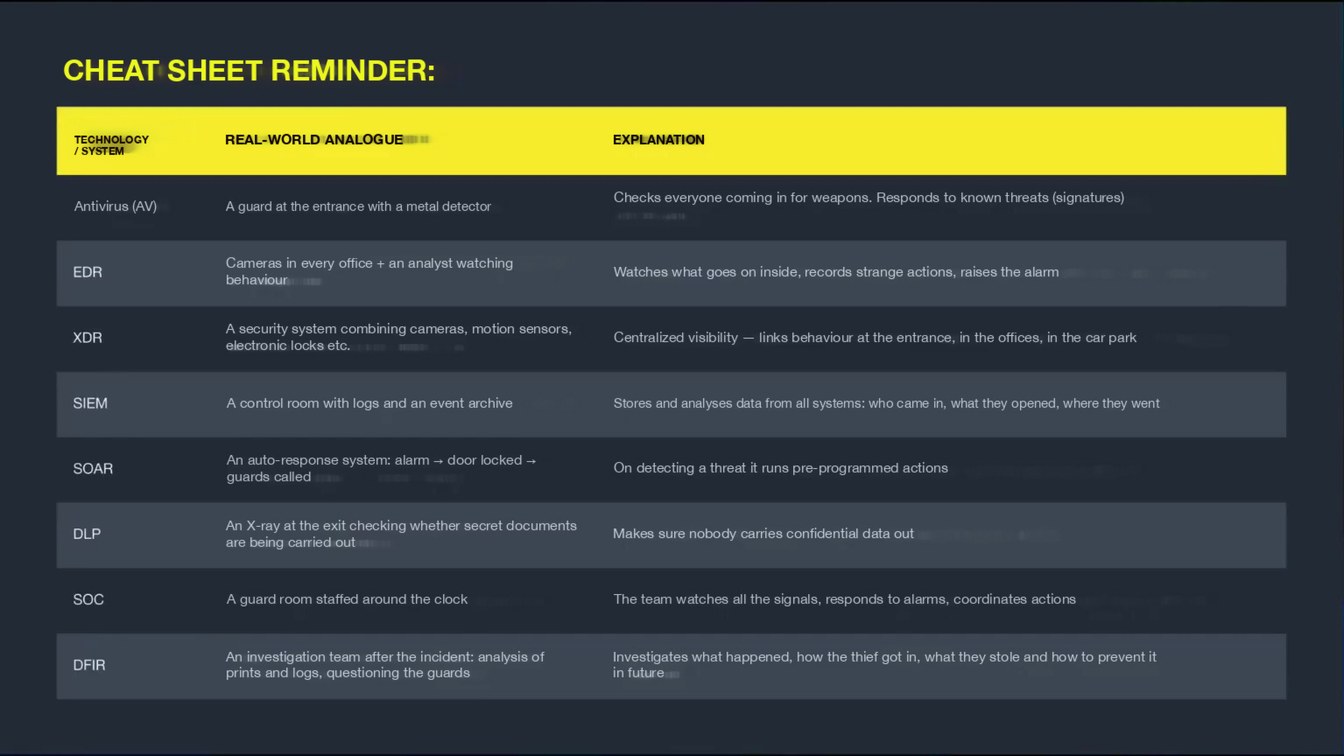
CHEAT SHEET REMINDER:
TECHNOLOGY / SYSTEM
REAL-WORLD ANALOGUE
EXPLANATION
Antivirus (AV)
A guard at the entrance with a metal detector
Checks everyone coming in for weapons. Responds to known threats (signatures)
EDR
Cameras in every office + an analyst watching behaviour
Watches what goes on inside, records strange actions, raises the alarm
XDR
A security system combining cameras, motion sensors, electronic locks etc.
Centralized visibility — links behaviour at the entrance, in the offices, in the car park
SIEM
A control room with logs and an event archive
Stores and analyses data from all systems: who came in, what they opened, where they went
SOAR
An auto-response system: alarm → door locked → guards called
On detecting a threat it runs pre-programmed actions
DLP
An X-ray at the exit checking whether secret documents are being carried out
Makes sure nobody carries confidential data out
SOC
A guard room staffed around the clock
The team watches all the signals, responds to alarms, coordinates actions
DFIR
An investigation team after the incident: analysis of prints and logs, questioning the guards
Investigates what happened, how the thief got in, what they stole and how to prevent it in future
Page 3106:24:58 Slide text
INSTEAD OF A CONCLUSION:
Don’t fall for bare advertising
Assess, consult, communicate, count everything in figures (don’t want to think — go to the pentesters)
Without a sensible approach any tool (even antivirus) is just an expensive toy that eats money and nerves
Page 3206:25:45 Slide text
THANK YOU
CONTACTS:
+7 (495) 909-92-78
clients@mko-systems.ru
mko-security.ru