Slides / 5 of 19
Talk slides
Applying forensic methods to investigate thefts committed with NFC technology
Alexey Moskvichev · MKO Systems
Day 1 — Thursday, 11 September 2025: digital forensics day · Scheduled 13:05–13:35 · In the recording 01:40:39–02:18:13
These slides are an English version of the Russian deck shown in the recording: the text the authors set in the presentation has been translated and redrawn in place, while everything captured from a screen — program windows, logs, evidence — is left exactly as it was, in Russian. The fonts are the closest available ones, not the originals. The Russian deck is on the RU version of this page. Under each slide its text is set out for word search and machine reading.
Page 101:41:43 Slide text
MOSCOW
FORENSICS
DAY '25
ALEXEY MOSKVICHEV
“APPLYING FORENSIC METHODS TO INVESTIGATE THEFTS COMMITTED WITH NFC TECHNOLOGY”
MKO SYSTEMS LLC
IVIL
100
MFD
MFD
Page 201:42:53 Slide text
NFC IS A SHORT-RANGE WIRELESS COMMUNICATION TECHNOLOGY THAT USES RADIO-FREQUENCY IDENTIFICATION TO RECOGNIZE OBJECTS AND DEVICES AND TO READ STORED INFORMATION
Short-range communication
Fast pairing
Low power consumption
Versatile applications
Page 301:45:48 Slide text
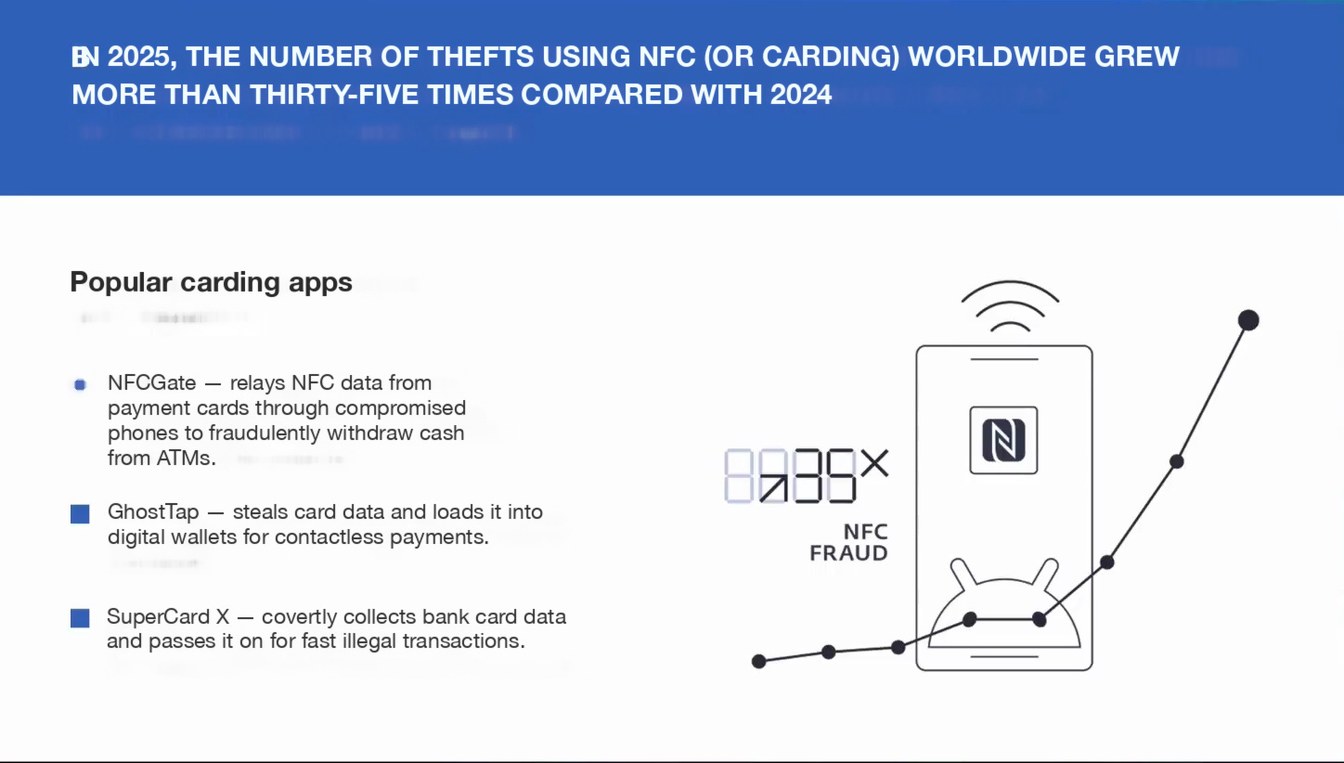
IN 2025, THE NUMBER OF THEFTS USING NFC (OR CARDING) WORLDWIDE GREW MORE THAN THIRTY-FIVE TIMES COMPARED WITH 2024
Popular carding apps
NFCGate — relays NFC data from payment cards through compromised phones to fraudulently withdraw cash from ATMs.
GhostTap — steals card data and loads it into digital wallets for contactless payments.
8938×
SuperCard X — covertly collects bank card data and passes it on for fast illegal transactions.
Page 401:48:53 Slide text
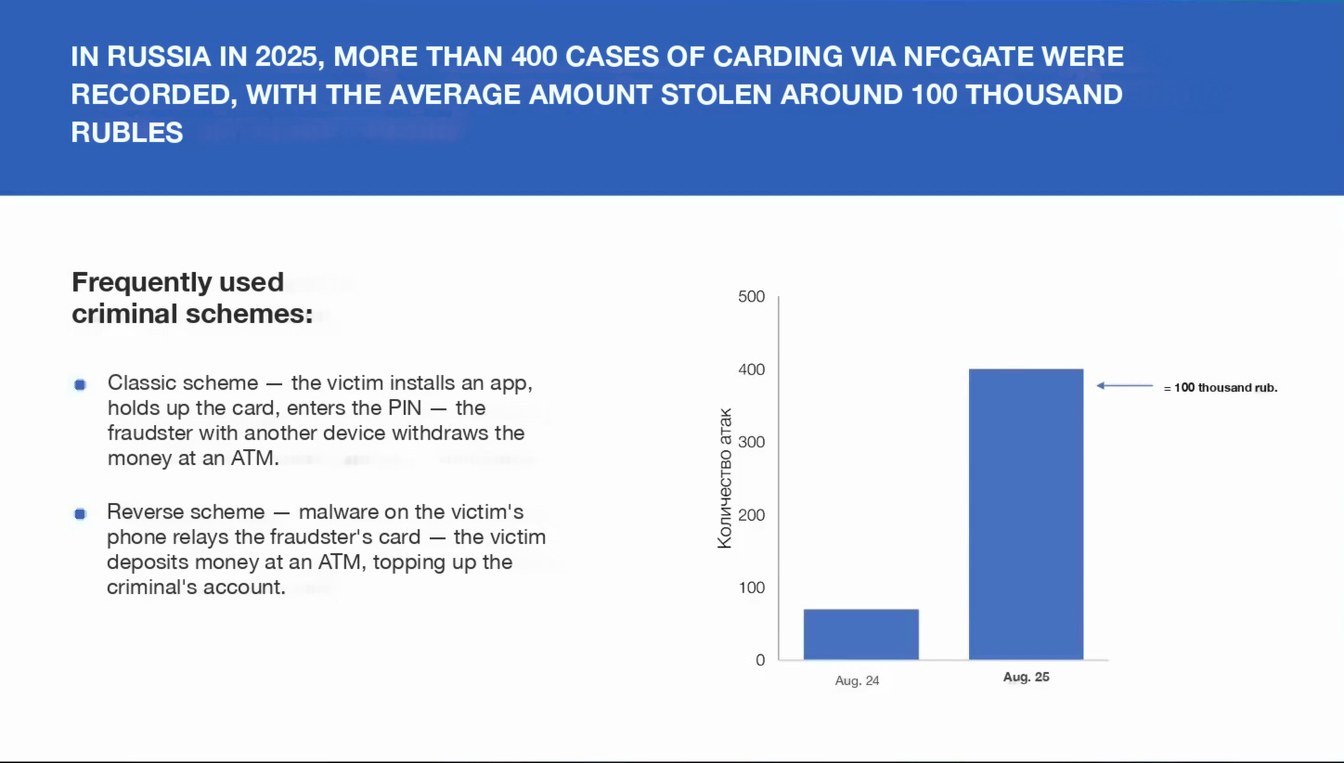
IN RUSSIA IN 2025, MORE THAN 400 CASES OF CARDING VIA NFCGATE WERE RECORDED, WITH THE AVERAGE AMOUNT STOLEN AROUND 100 THOUSAND RUBLES
Frequently used criminal schemes:
500
Classic scheme — the victim installs an app, holds up the card, enters the PIN — the fraudster with another device withdraws the money at an ATM.
400
300
ТВО
= 100 thousand rub.
Reverse scheme — malware on the victim's phone relays the fraudster's card — the victim deposits money at an ATM, topping up the criminal's account.
· 200
100
Aug. 24
Aug. 25
Page 501:52:42 Slide text
IN RUSSIA IN 2025, MORE THAN 400 CASES OF CARDING VIA NFCGATE WERE RECORDED, WITH THE AVERAGE AMOUNT STOLEN AROUND 100 THOUSAND RUBLES
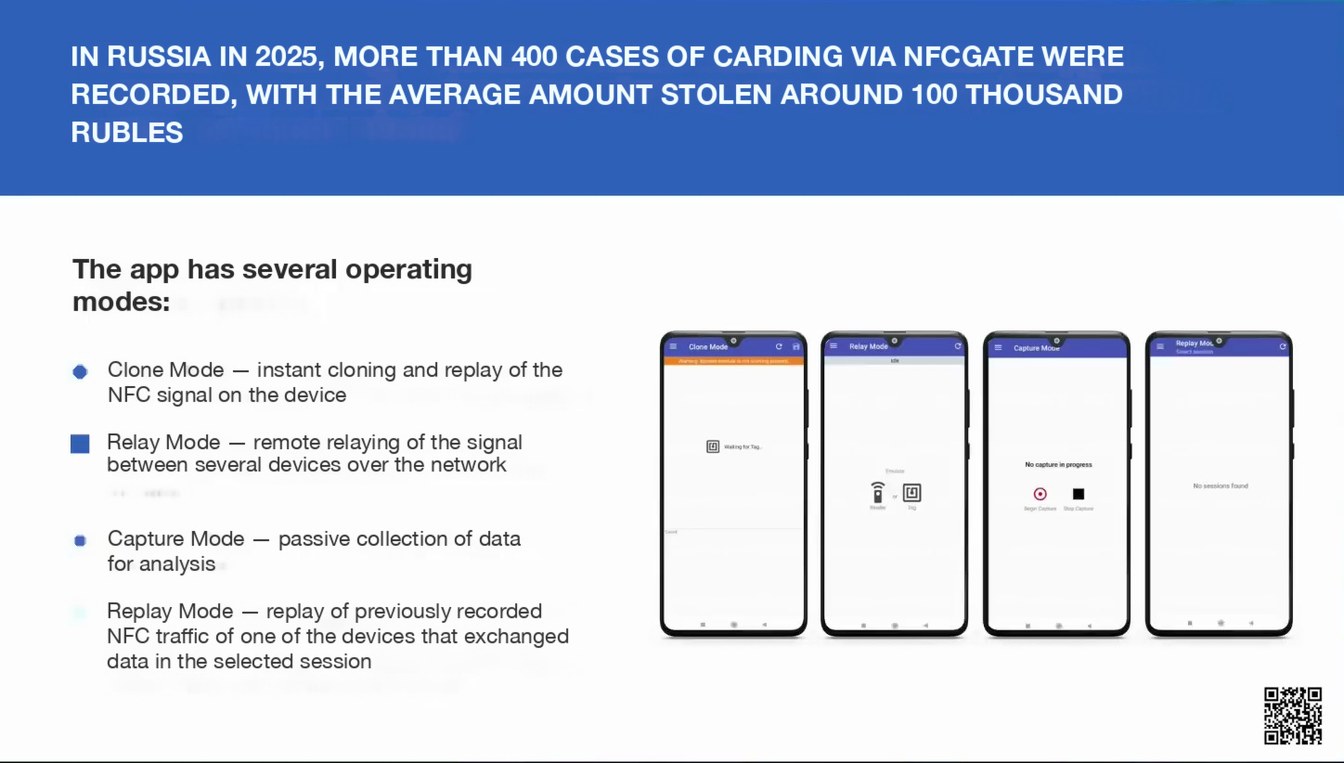
The app has several operating modes:
Clone Mode — instant cloning and replay of the NFC signal on the device
• Clone Mode o c a
Relay Modo Oa
= Capte Mocie
-Rapay Mo. 0
Relay Mode — remote relaying of the signal between several devices over the network
Wiad ing for Tag
No capture in progress
Capture Mode — passive collection of data for analysis
Replay Mode — replay of previously recorded NFC traffic of one of the devices that exchanged data in the selected session
Page 601:57:31 Slide text
NFCGATE IN ACTION: MAN-IN-THE-MIDDLE ATTACKS USING THE RELAY AND REPLAY MODES
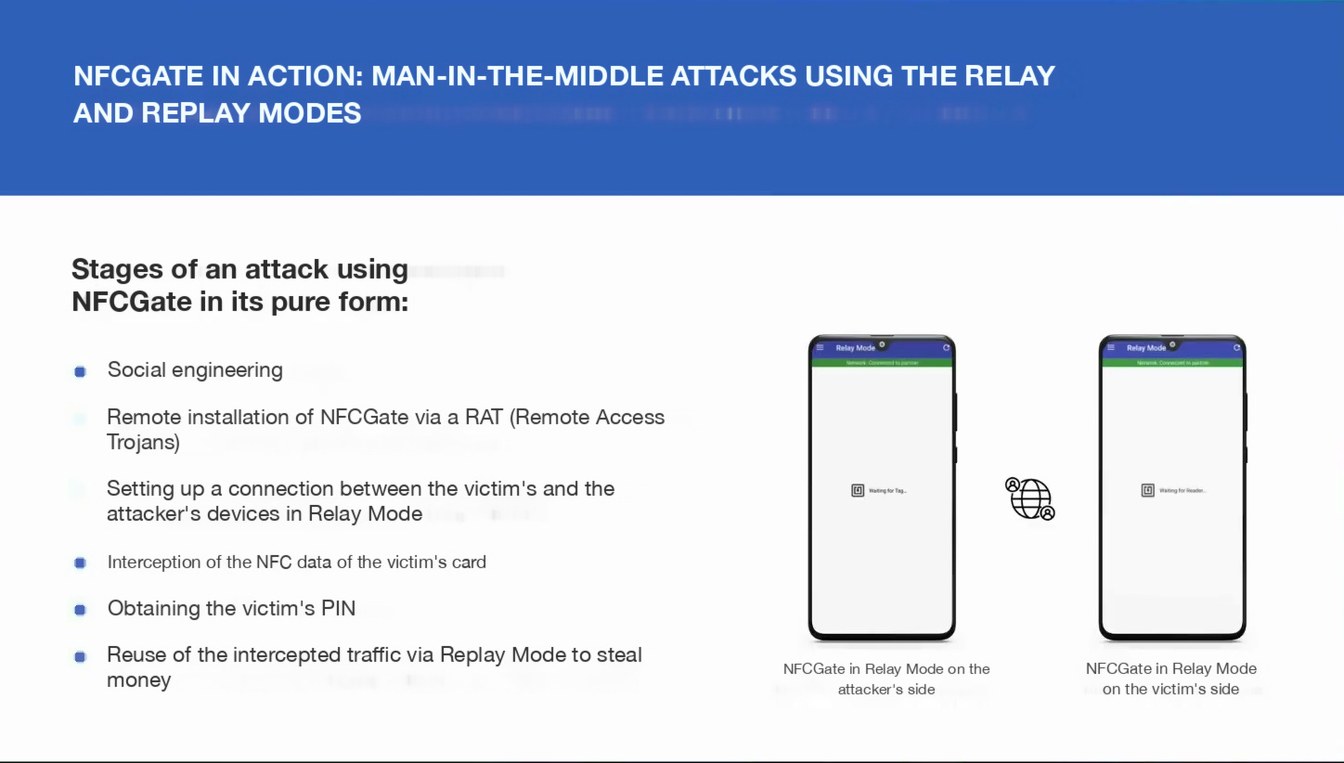
Stages of an attack using NFCGate in its pure form:
Social engineering
Relay Mode O
• Relay Mode °
Remote installation of NFCGate via a RAT (Remote Access Trojans) Setting up a connection between the victim's and the attacker's devices in Relay Mode
1) ming to Seated
Interception of the NFC data of the victim's card
Obtaining the victim's PIN
Reuse of the intercepted traffic via Replay Mode to steal money
NFCGate in Relay Mode on the attacker's side
NFCGate in Relay Mode on the victim's side
Page 702:00:52 Slide text
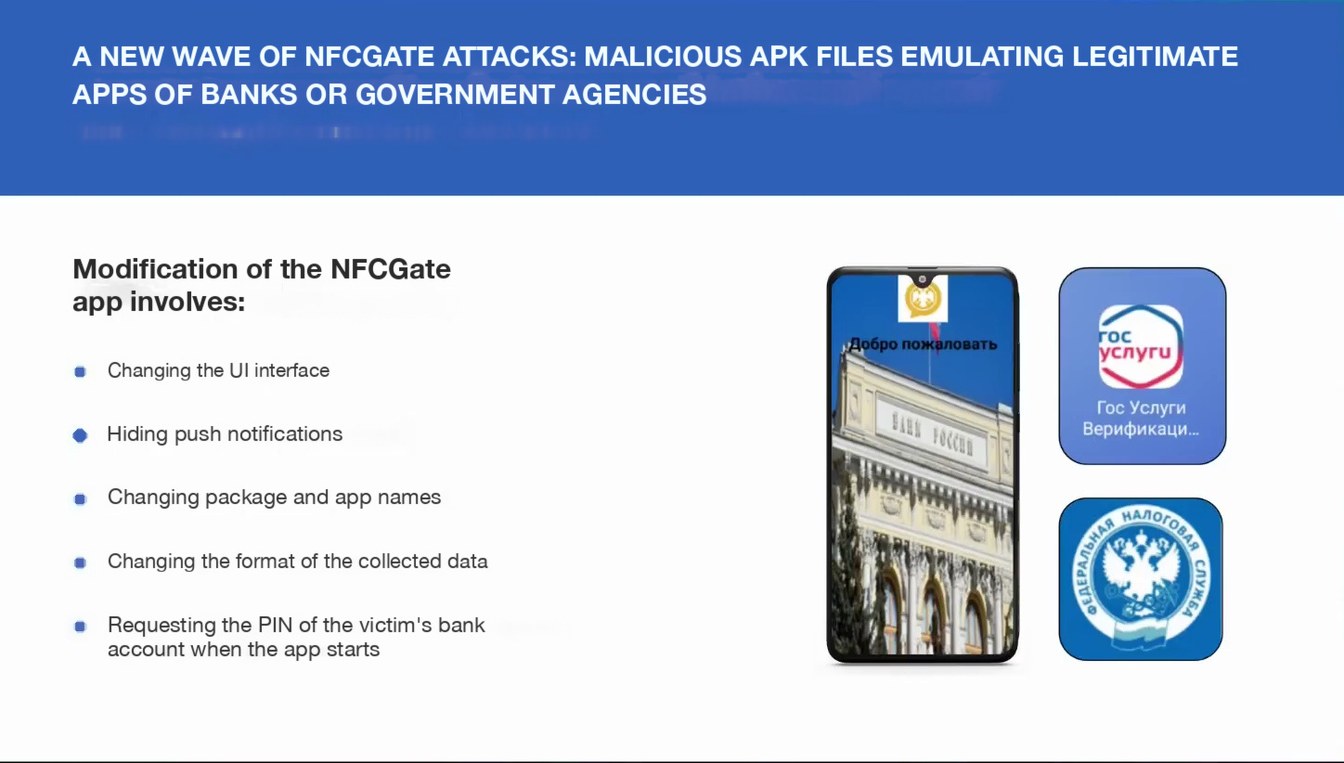
A NEW WAVE OF NFCGATE ATTACKS: MALICIOUS APK FILES EMULATING LEGITIMATE APPS OF BANKS OR GOVERNMENT AGENCIES
Modification of the NFCGate app involves:
Changing the UI interface
Hiding push notifications
• Добро пожаловать
гос
услуги
Гос Услуги Верификаци...
Changing package and app names
Changing the format of the collected data
Requesting the PIN of the victim's bank account when the app starts
ФЕДЕРАЛЬНАВ
СЛУЖБА
Page 802:02:01 Slide text
CASE
INCIDENT OUTLINE (22.01.2025)
A call on Telegram from an unknown person posing as a law enforcement officer
Pretext:
“Keeping the money safe”
Attacker's actions:
A request to install an unknown app
Instructions to launch it and hold a bank card up to the phone
Advice to delete the app
Result:
Withdrawal of 230,000 rub. from the card at an ATM by a third party
Subject of the examination:
Redmi Note 11S mobile phone
Page 902:03:02 Slide text
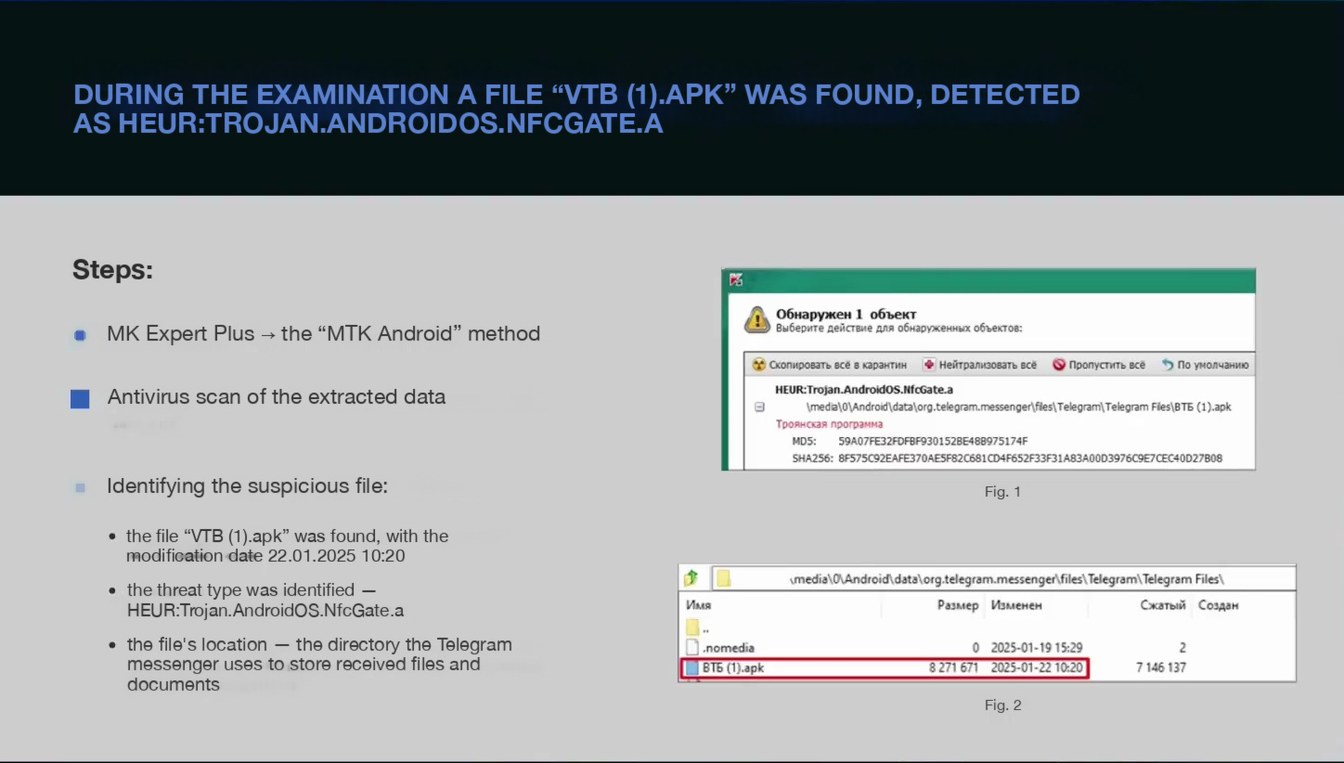
DURING THE EXAMINATION A FILE “VTB (1).APK” WAS FOUND, DETECTED AS HEUR:TROJAN.ANDROIDOS.NFCGATE.A
Steps:
MK Expert Plus → the “MTK Android” method
Antivirus scan of the extracted data
Identifying the suspicious file:
Обнаружен 1 объект Выберите действие для обнаруженных объектов:
) Скопировать всё в карантин
• Нейтрализовать всё
Пропустить всё
• По умолчанию
HEUR:Trojan.AndroidOS.NfcGate.a
(media\0\Android\data\org.telegram.messenger\fles\Telegram) Telegram Fies\BT (1).apk
Троянская программа
MD5:
59A07FE32FDFBF930152BE488975174F
SHA256: 8F575C92EAFE370AESF82C681CD4F652F33F31A83A00D3976C9E7CEC40D27B08
Fig. 1
the file “VTB (1).apk” was found, with the modification date 22.01.2025 10:20
the threat type was identified — HEUR:Trojan.AndroidOS.NfcGate.a
Имя
media\0\Android \data\org.telegram.messenger\files\Telegram\ Telegram Files\
Сжатый Создан
Размер
Изменен
the file's location — the directory the Telegram messenger uses to store received files and documents
.nomedia
B16 (1).apk
0 2025-01-19 15:29
8 271 671
2025-01-22 10:20
Fig. 2
2
7146 137
Page 1002:04:08 Slide text
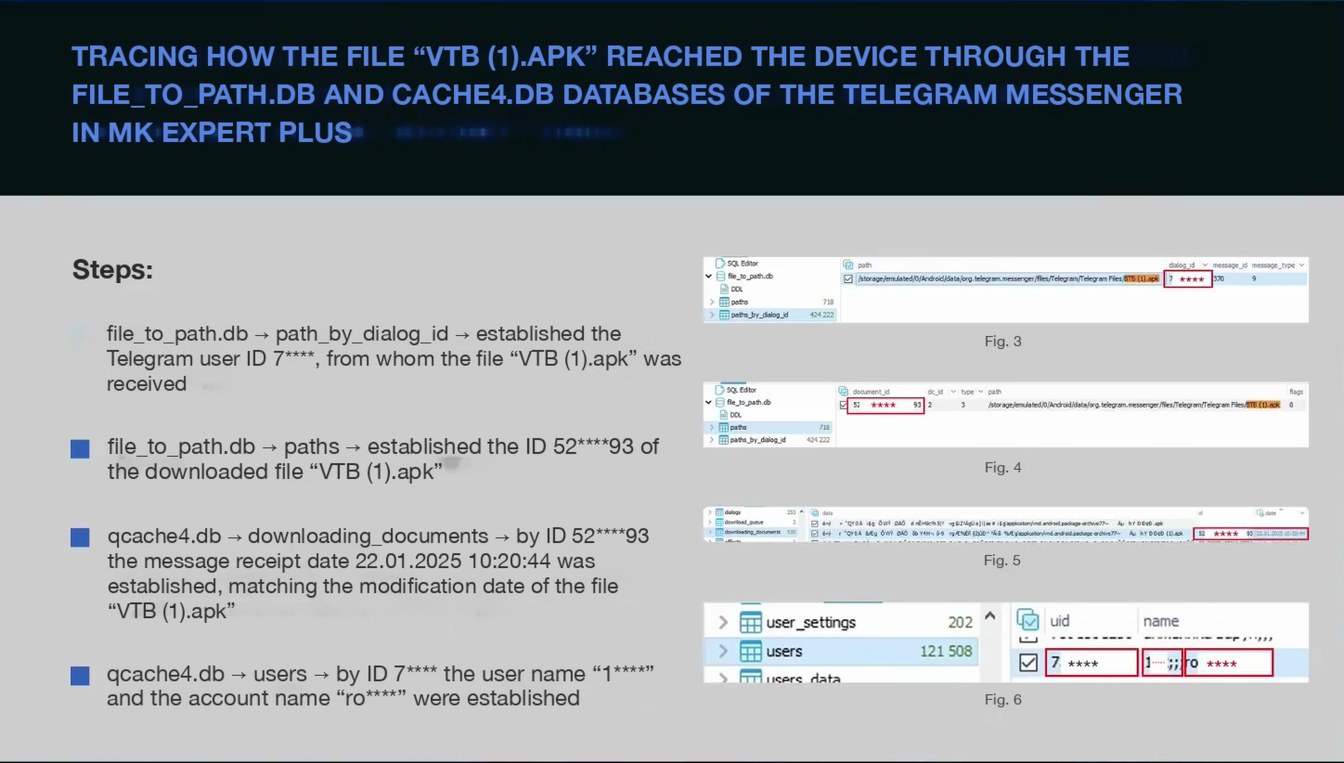
TRACING HOW THE FILE “VTB (1).APK” REACHED THE DEVICE THROUGH THE FILE_TO_PATH.DB AND CACHE4.DB DATABASES OF THE TELEGRAM MESSENGER IN MK EXPERT PLUS
Steps:
L SQL Editor
4 path
message_d message_type
vE fle_to_path.do
storege /emulated/0/Android/dato/org.telegram.messenger/fles/Telegram/TelegramFles, 816(1) a **** 1330
> Epoths > peths_by_dolog_id
424 222
file_to_path.db → path_by_dialog_id → established the Telegram user ID 7****, from whom the file “VTB (1).apk” was received
Fig. 3
• so. Edtor vE fle_to_asth.do
**** 93 2
/stor age/emulated/0/Andraid/data/org.telegrem.messenger/fies/Telegram/TelegramFiles/8T6(D.ok 0
E oxx
file_to_path.db → paths → established the ID 52****93 of the downloaded file “VTB (1).apk”
424 222
Fig. 4
qcache4.db → downloading_documents → by ID 52****93 the message receipt date 22.01.2025 10:20:44 was established, matching the modification date of the file “VTB (1).apk”
qcache4.db → users → by ID 7**** the user name “1****” and the account name “ro****” were established
user_settings
users
TRucers data
Fig. 5
Guid
202
121 508
Fig. 6
name
110****
Page 1102:05:34 Slide text
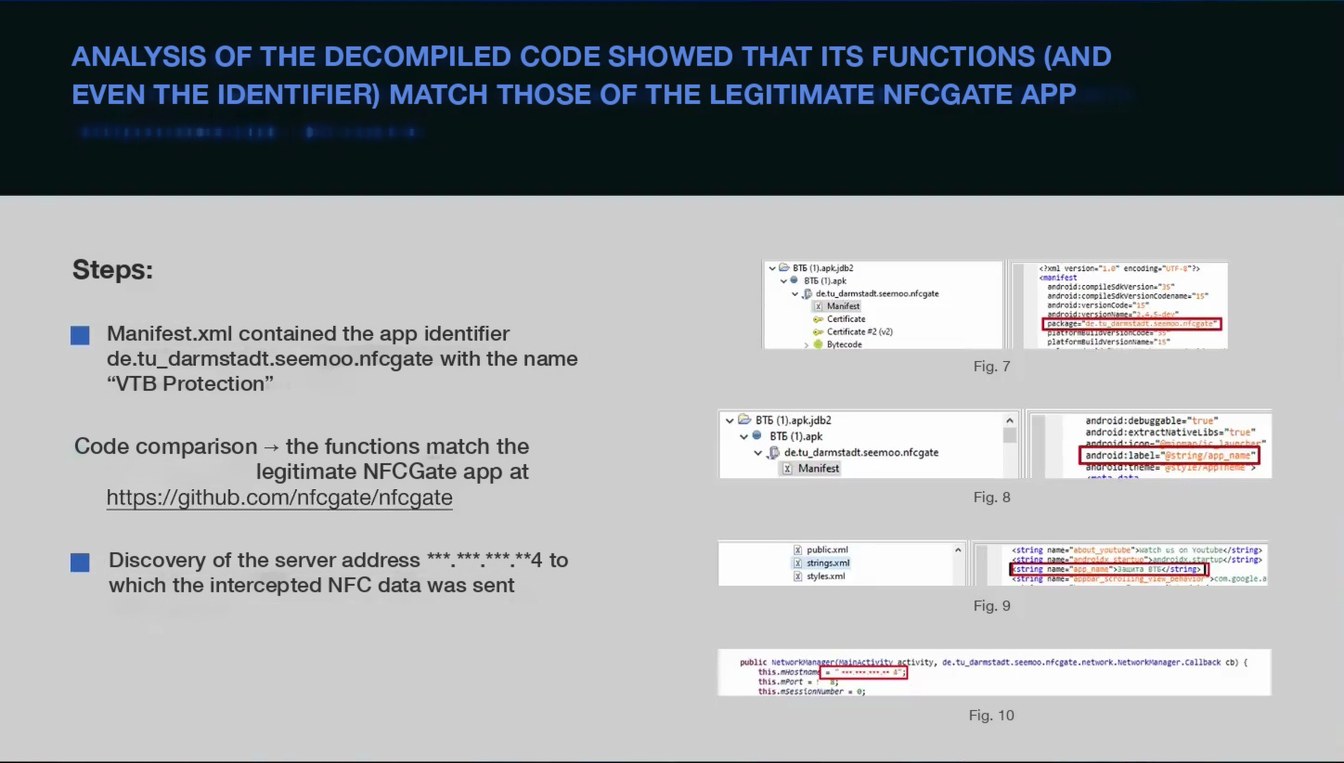
ANALYSIS OF THE DECOMPILED CODE SHOWED THAT ITS FUNCTIONS (AND EVEN THE IDENTIFIER) MATCH THOSE OF THE LEGITIMATE NFCGATE APP
Steps:
Manifest.xml contained the app identifier de.tu_darmstadt.seemoo.nfcgate with the name “VTB Protection”
v@ BT6 (1).apk.jdb2
<}xn1 version*"1,e" encoding-"UTF-§"?> manifest
ve 8T6 (1).apk v. de.tu_darmstadt.seemoo.nfcgate
android: conpilesdkversionCodenane="15"
x Manifest
android: versionCode="15)
e Certificate •* Certificate =2 (v2) • Bytecode
Fig. 7
Code comparison → the functions match the legitimate NFCGate app at
https://github.com/nfcgate/nfcgate
v 2 BT6 (1).apk.jdb2 v • ВТБ (1).apk v.@de.tu_darmstadt.seemoo.nfcgate
x Manifest
Fig. 8
android: debuggable="true"
android: extractativelibs="true"
android: label="estring/app_name
Discovery of the server address ***.***.***.**4 to which the intercepted NFC data was sent
* public.xml X) strings.xml * styles.xml
kstring name«"app nal
1а 0/string
>com.google.a
Fig. 9
this. asessiontumber = 0;
Fig. 10
Page 1202:06:23 Slide text
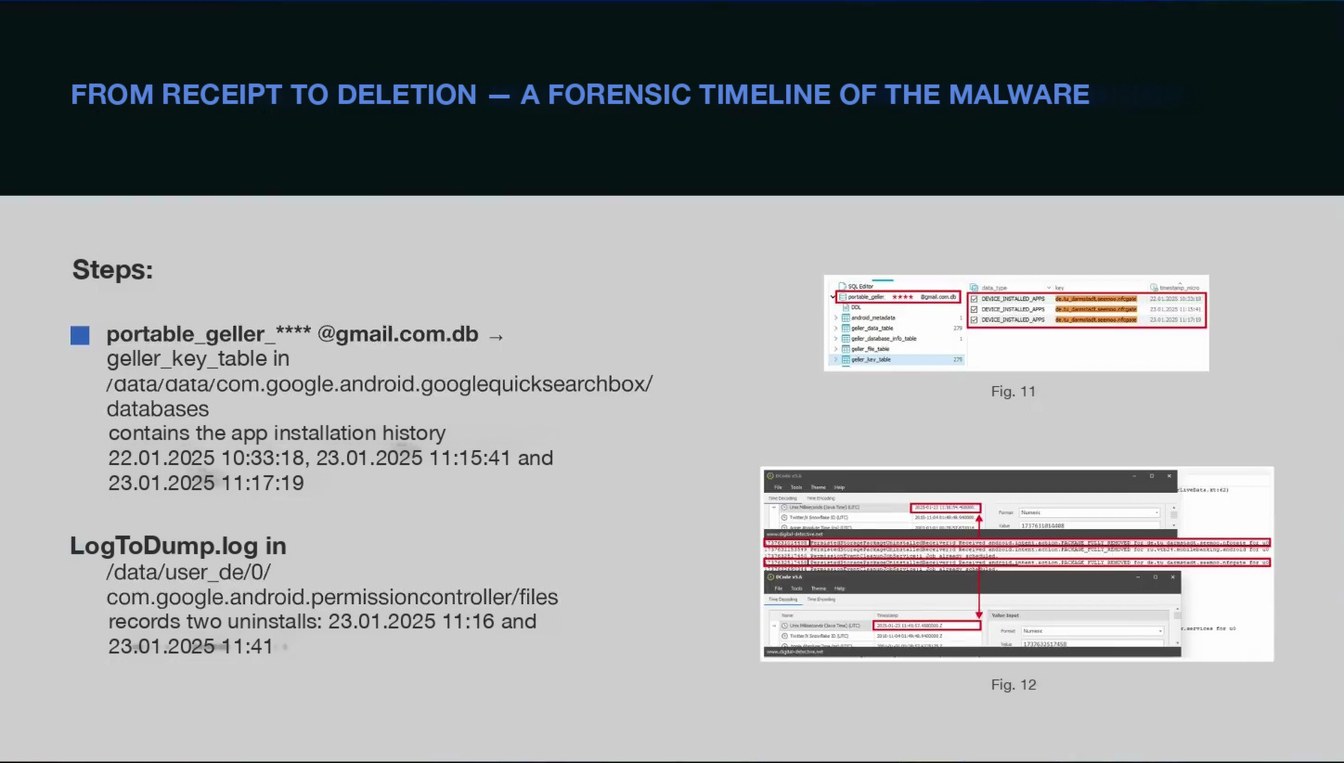
FROM RECEIPT TO DELETION — A FORENSIC TIMELINE OF THE MALWARE
Steps:
• portable_geller ****@gmail.com.db →
geller_key_table in /data/data/com.google.android.googlequicksearchbox/ databases
contains the app installation history 22.01.2025 10:33:18, 23.01.2025 11:15:41 and 23.01.2025 11:17:19
→ SQL Editor
> El andrad, metadets • seler_500,004 > Fooler _dosabase, info_table > Epeter fle table En peder_ber Joble
• DEVICE, INSTALLED APPS
Fig. 11
23.01.2025 11:15:41
LogToDump.log in
/data/user_de/0/ com.google.android.permissioncontroller/files
records two uninstalls: 23.01.2025 11:16 and 23.01.2025 11:41
He Tools Theme Melt
Fig. 12
Page 1302:07:05 Slide text
FROM RECEIPT TO DELETION — A FORENSIC TIMELINE OF THE MALWARE
Steps:
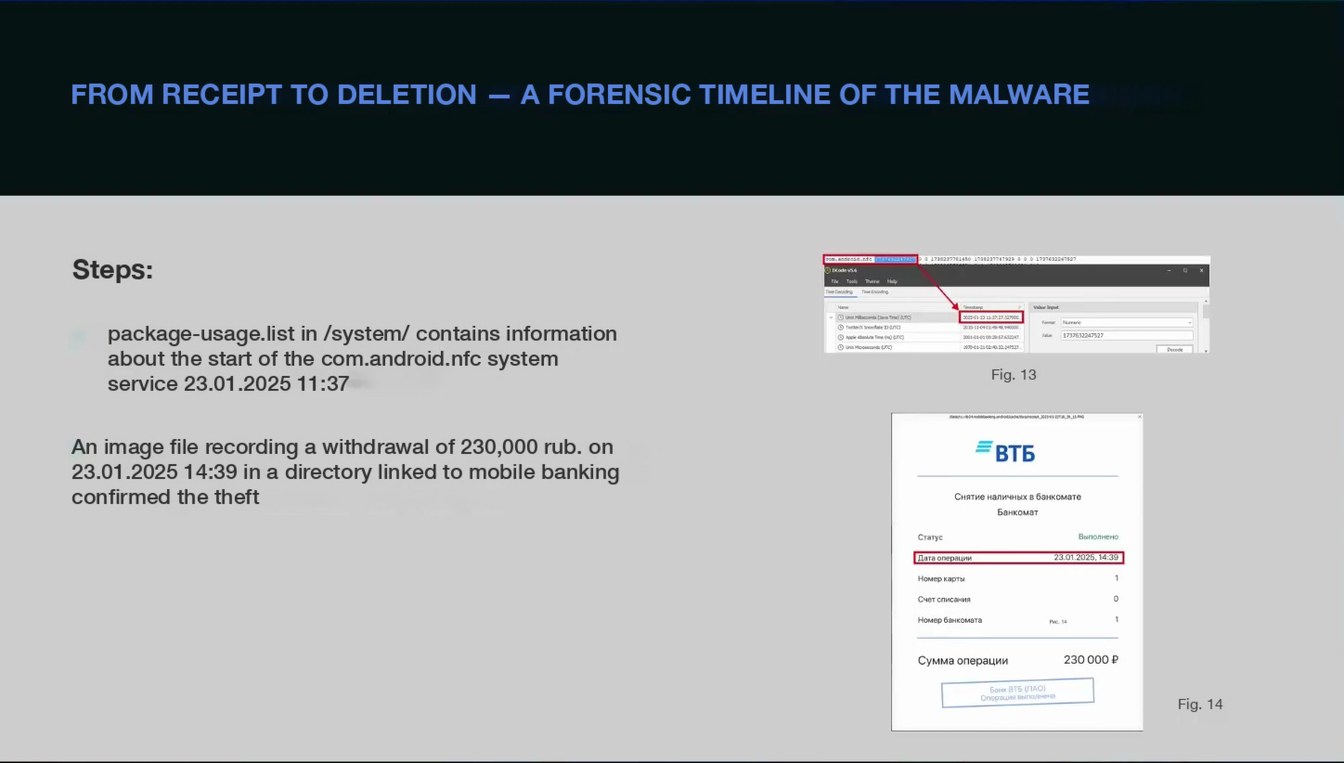
package-usage.list in /system/ contains information about the start of the com.android.nfc system service 23.01.2025 11:37
- uca (lea Thel ATC © тып setue DaNO
unt ml
Exas01 23 11a7.27.427300
tamar
-Numeie
5737632247527
208036800-8430
Fig. 13
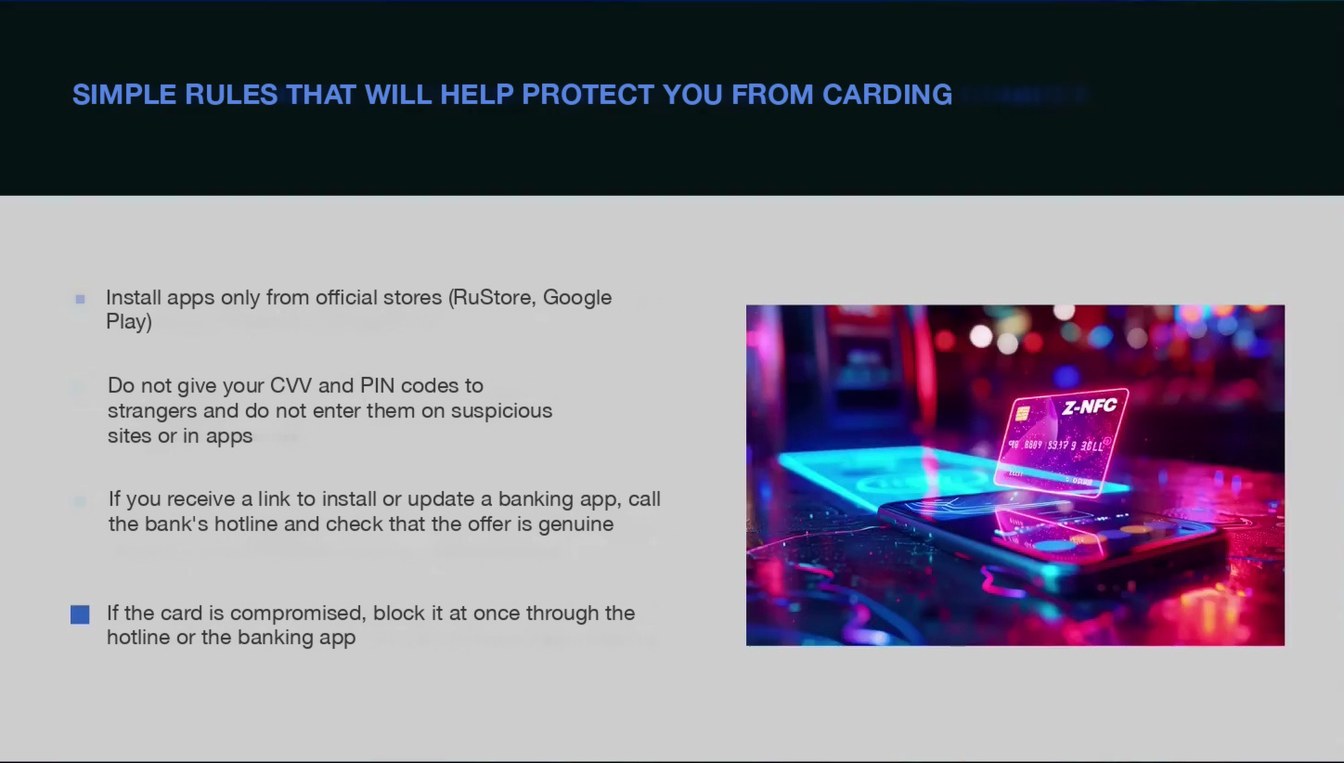
An image file recording a withdrawal of 230,000 rub. on 23.01.2025 14:39 in a directory linked to mobile banking confirmed the theft
= ВТБ
Снятие наличных в банкомате
Банкомат
Статус
Дата операции
Номер карты
Счет списания
Номер банкомата
23.01.2025, 14:39
Pe. 1
Сумма операции
230 000 ₽
Банк ВТБ (ПАО) Операция выполне
Fig. 14
Page 1402:07:54 Slide text
SIMPLE RULES THAT WILL HELP PROTECT YOU FROM CARDING
Install apps only from official stores (RuStore, Google Play)
Do not give your CVV and PIN codes to strangers and do not enter them on suspicious sites or in apps
Z-NFC
98,8899 $9173 26LLº
If you receive a link to install or update a banking app, call the bank's hotline and check that the offer is genuine
If the card is compromised, block it at once through the hotline or the banking app
Page 1502:08:30 Slide text
The financial abyss is the deepest of all abysses, you can fall into it all your life.
O. Bender